Inside the $6.3 Billion Binance Hack: What Happened, Who Was Hit, and What It Means

Infographic illustrating the $6.3 billion Binance hack in October 2026.

Figure 1. The $6.3 Billion Binance Hack Title Infographic. Jeremy Swenson. October 2026.

On Thursday night, the world’s largest cryptocurrency exchange suffered what is now the largest theft in the industry’s history. Roughly $6.3 billion in digital assets left Binance’s hot wallets in a matter of minutes, more than four times the $1.5 billion taken from the exchange Bybit in February 2025, the previous record.[1] What follows is what we know so far, what it means for customers, including users of Binance.US, and the lessons that security, risk, and finance leaders should take from it.

What Happened

On the evening of October 29, on-chain researchers began flagging unusually large outflows from Binance wallets. Within the hour, Binance co-founder Changpeng Zhao acknowledged publicly that the activity looked like a hack, and the exchange paused withdrawals across multiple networks.[2] The blockchain analytics firm TRM Labs estimates that approximately $6.36 billion was moved out of Binance wallets across ten blockchains, most of it within about twenty minutes.[3] Binance’s own estimate puts the total impact at about $6.3 billion, and the company has cautioned that the figure may rise as tracing continues.[4]
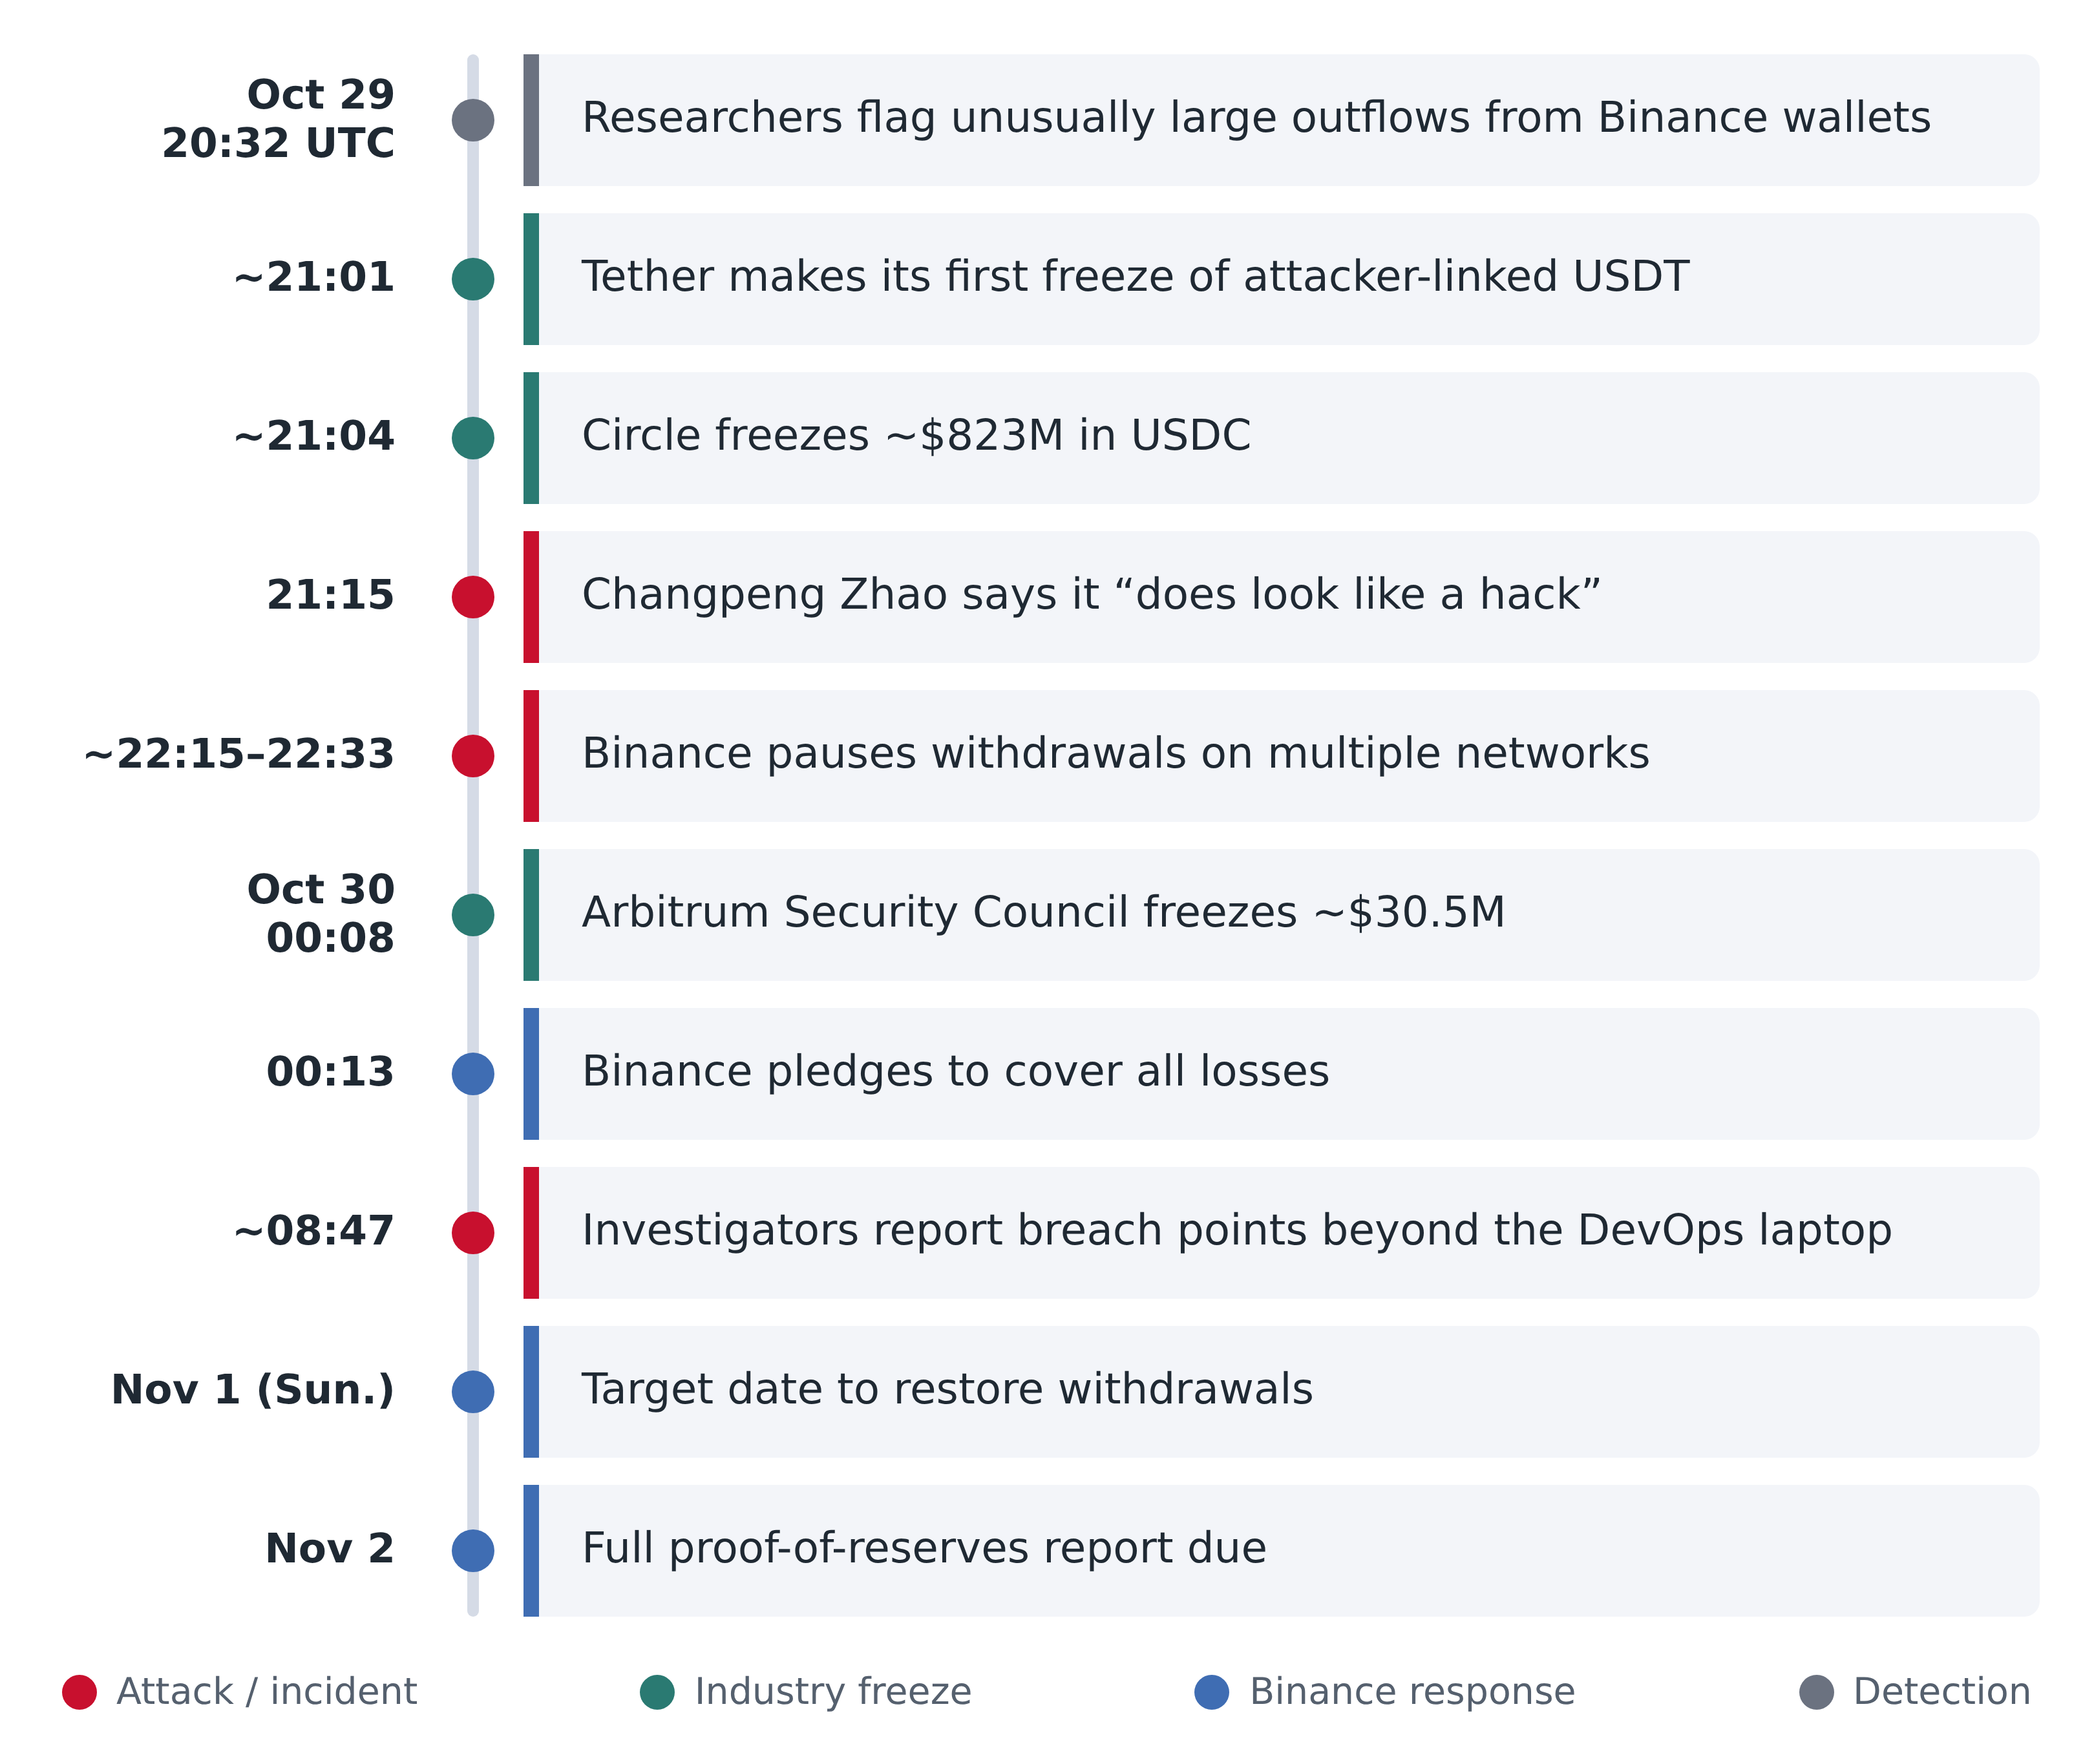
Timeline infographic depicting the Binance hack from October 29 through November 2, 2026. Events are presented in approximate Coordinated Universal Time (UTC), noting that reported times vary across sources.

Figure 2. Timeline of the Binance hack, October 29–November 2, 2026. Times are approximate and in Coordinated Universal Time (UTC); reported times differ across sources. Jeremy Swenson. Data from Crypto Times, HackenProof, Bloomingbit, and statements by Binance, Tether, Circle, and the Arbitrum Security Council.[5] October 2026.

How the Attackers Got In

Binance’s first explanation pointed to a single entry point: a compromised laptop belonging to a DevOps engineer, which reportedly allowed the attacker to reach a service container and submit unauthorized withdrawal transactions.[6] That picture has since grown more complicated. Co-CEO Richard Teng has said the breach was not a one-click event but a more complex, multistage attack, and Binance’s investigators have identified additional points of breach beyond the laptop.[7] Teng also stated that the team had found no evidence that any wallet private keys were leaked.[8] Teng has also said the attackers used a self-destruct mechanism that erased their tooling and traces as they went, which has made reconstructing the intrusion more difficult.[9]

Not every analysis aligns neatly with that account. The security firm Blockaid’s incident report indicates that eleven Binance hot-wallet keys signed the outgoing transfers, which raises the question of whether the attacker abused Binance’s signing infrastructure rather than stealing keys outright.[10] Binance has promised a full technical post-mortem once its investigation is complete, and that report should reconcile the competing accounts.[11]

Speed and Automation

The pace of the attack stands out as much as its size. In a research report released Friday, Chainalysis found that the attackers not only moved the funds quickly but also laundered the proceeds and destroyed evidence of their operation at an unprecedented speed, a pattern its researchers read as automation running through the entire heist.[12] Eric Jardine, head of research at Chainalysis, told Axios that the transactions came at a frequency and scale that ruled out any person approving them: “It had to have been done by a computer.”[13] Researchers at TRM Labs also found that the attackers began preparing for the operation only about 36 hours before it was launched.[14]

Who Is Behind It

Neither Binance nor the FBI has formally attributed the attack.[15] Two prominent analytics firms, however, point in the same direction. TRM Labs links the theft to a North Korean state-sponsored group, citing hallmarks of earlier operations attributed to that country, including transaction signatures obtained in advance.[16] Several blockchain investigation firms have tied the theft specifically to TraderTraitor, a unit linked to the North Korean government’s Lazarus Group collective and the same group that set the previous record with the $1.5 billion Bybit theft.[17] Elliptic likewise assesses North Korea as the likely culprit and reports that some of the stolen funds reached an address connected to the laundering of a suspected North Korean exploit of the exchange Bitget, though Elliptic notes that this establishes a shared laundering network rather than proving a single attacker.[18] According to a person familiar with the matter cited by Reuters, Binance is working with the FBI and the U.S. Secret Service.[19]

A Decade of North Korean Financial Theft

If the attribution holds, the Binance theft extends a record of state-directed financial crime that stretches back more than a decade. In 2016, North Korean hackers tried to steal nearly $1 billion from Bangladesh’s central bank and got away with $81 million; in 2017, the country was blamed for the WannaCry ransomware outbreak, which disrupted hundreds of thousands of computers in more than 150 countries.[20] Pyongyang has since shifted its focus toward crypto exchanges, partly because digital assets are easier to move and launder across borders, even though such attacks tend to leave a more visible trail on-chain.[21] According to Chainalysis’s Jardine, North Korean operators now take the bulk of the value stolen in any given year, effectively crowding out other threat actors.[22]

The AI Accelerant

Experts warn that the speed on display at Binance may offer a glimpse of how artificial intelligence could further amplify North Korea’s operations. Vijay Balasubramaniyan, chief executive and co-founder of Pindrop Security, said social engineering and automation have become hallmarks of the country’s recent cyberattacks. He added that advances in AI-generated video and audio have enabled North Korean operatives to greatly expand schemes that trick U.S. companies into hiring them for IT jobs.[23] Across Pindrop’s customer base, North Korean applicants accounted for roughly one in every 343 job applications last year; this year the figure is about one in 47. Balasubramaniyan attributes the jump less to any single tool than to the sheer number, low cost, and growing ecosystem of AI tools now available to attackers.[24]

The Industry’s Freeze Response

One of the most striking features of this episode is how quickly the rest of the industry moved. Because a large share of the stolen funds were stablecoins, their issuers were able to freeze them on-chain:[25]

  • Tether froze more than $1.56 billion in USDT linked to the incident.[26]
  • Circle froze more than $800 million in USDC, in coordination with law enforcement.[27]
  • Ripple froze roughly $200 million, and World Liberty Financial, working with the custodian BitGo, froze stablecoins and its own tokens.[28]
  • Arbitrum’s Security Council froze about $30.5 million on its network, and the lending protocol Aave froze its Avalanche markets.[29]

Elliptic reports that stablecoins accounted for about $3.46 billion of the stolen funds and that the attacker was slow to convert them, which gave issuers a window in which to act. The firm has independently verified about $2.84 billion of frozen funds on-chain, close to Binance’s estimate of roughly $3 billion.[30] Binance has not said what has become of the remaining $3.3 billion.[31] Jardine said investigators may still recover some of the unfrozen half if those funds pass through exchange infrastructure whose operators can move quickly enough to freeze them, though he cautioned that it is still early days.[32]
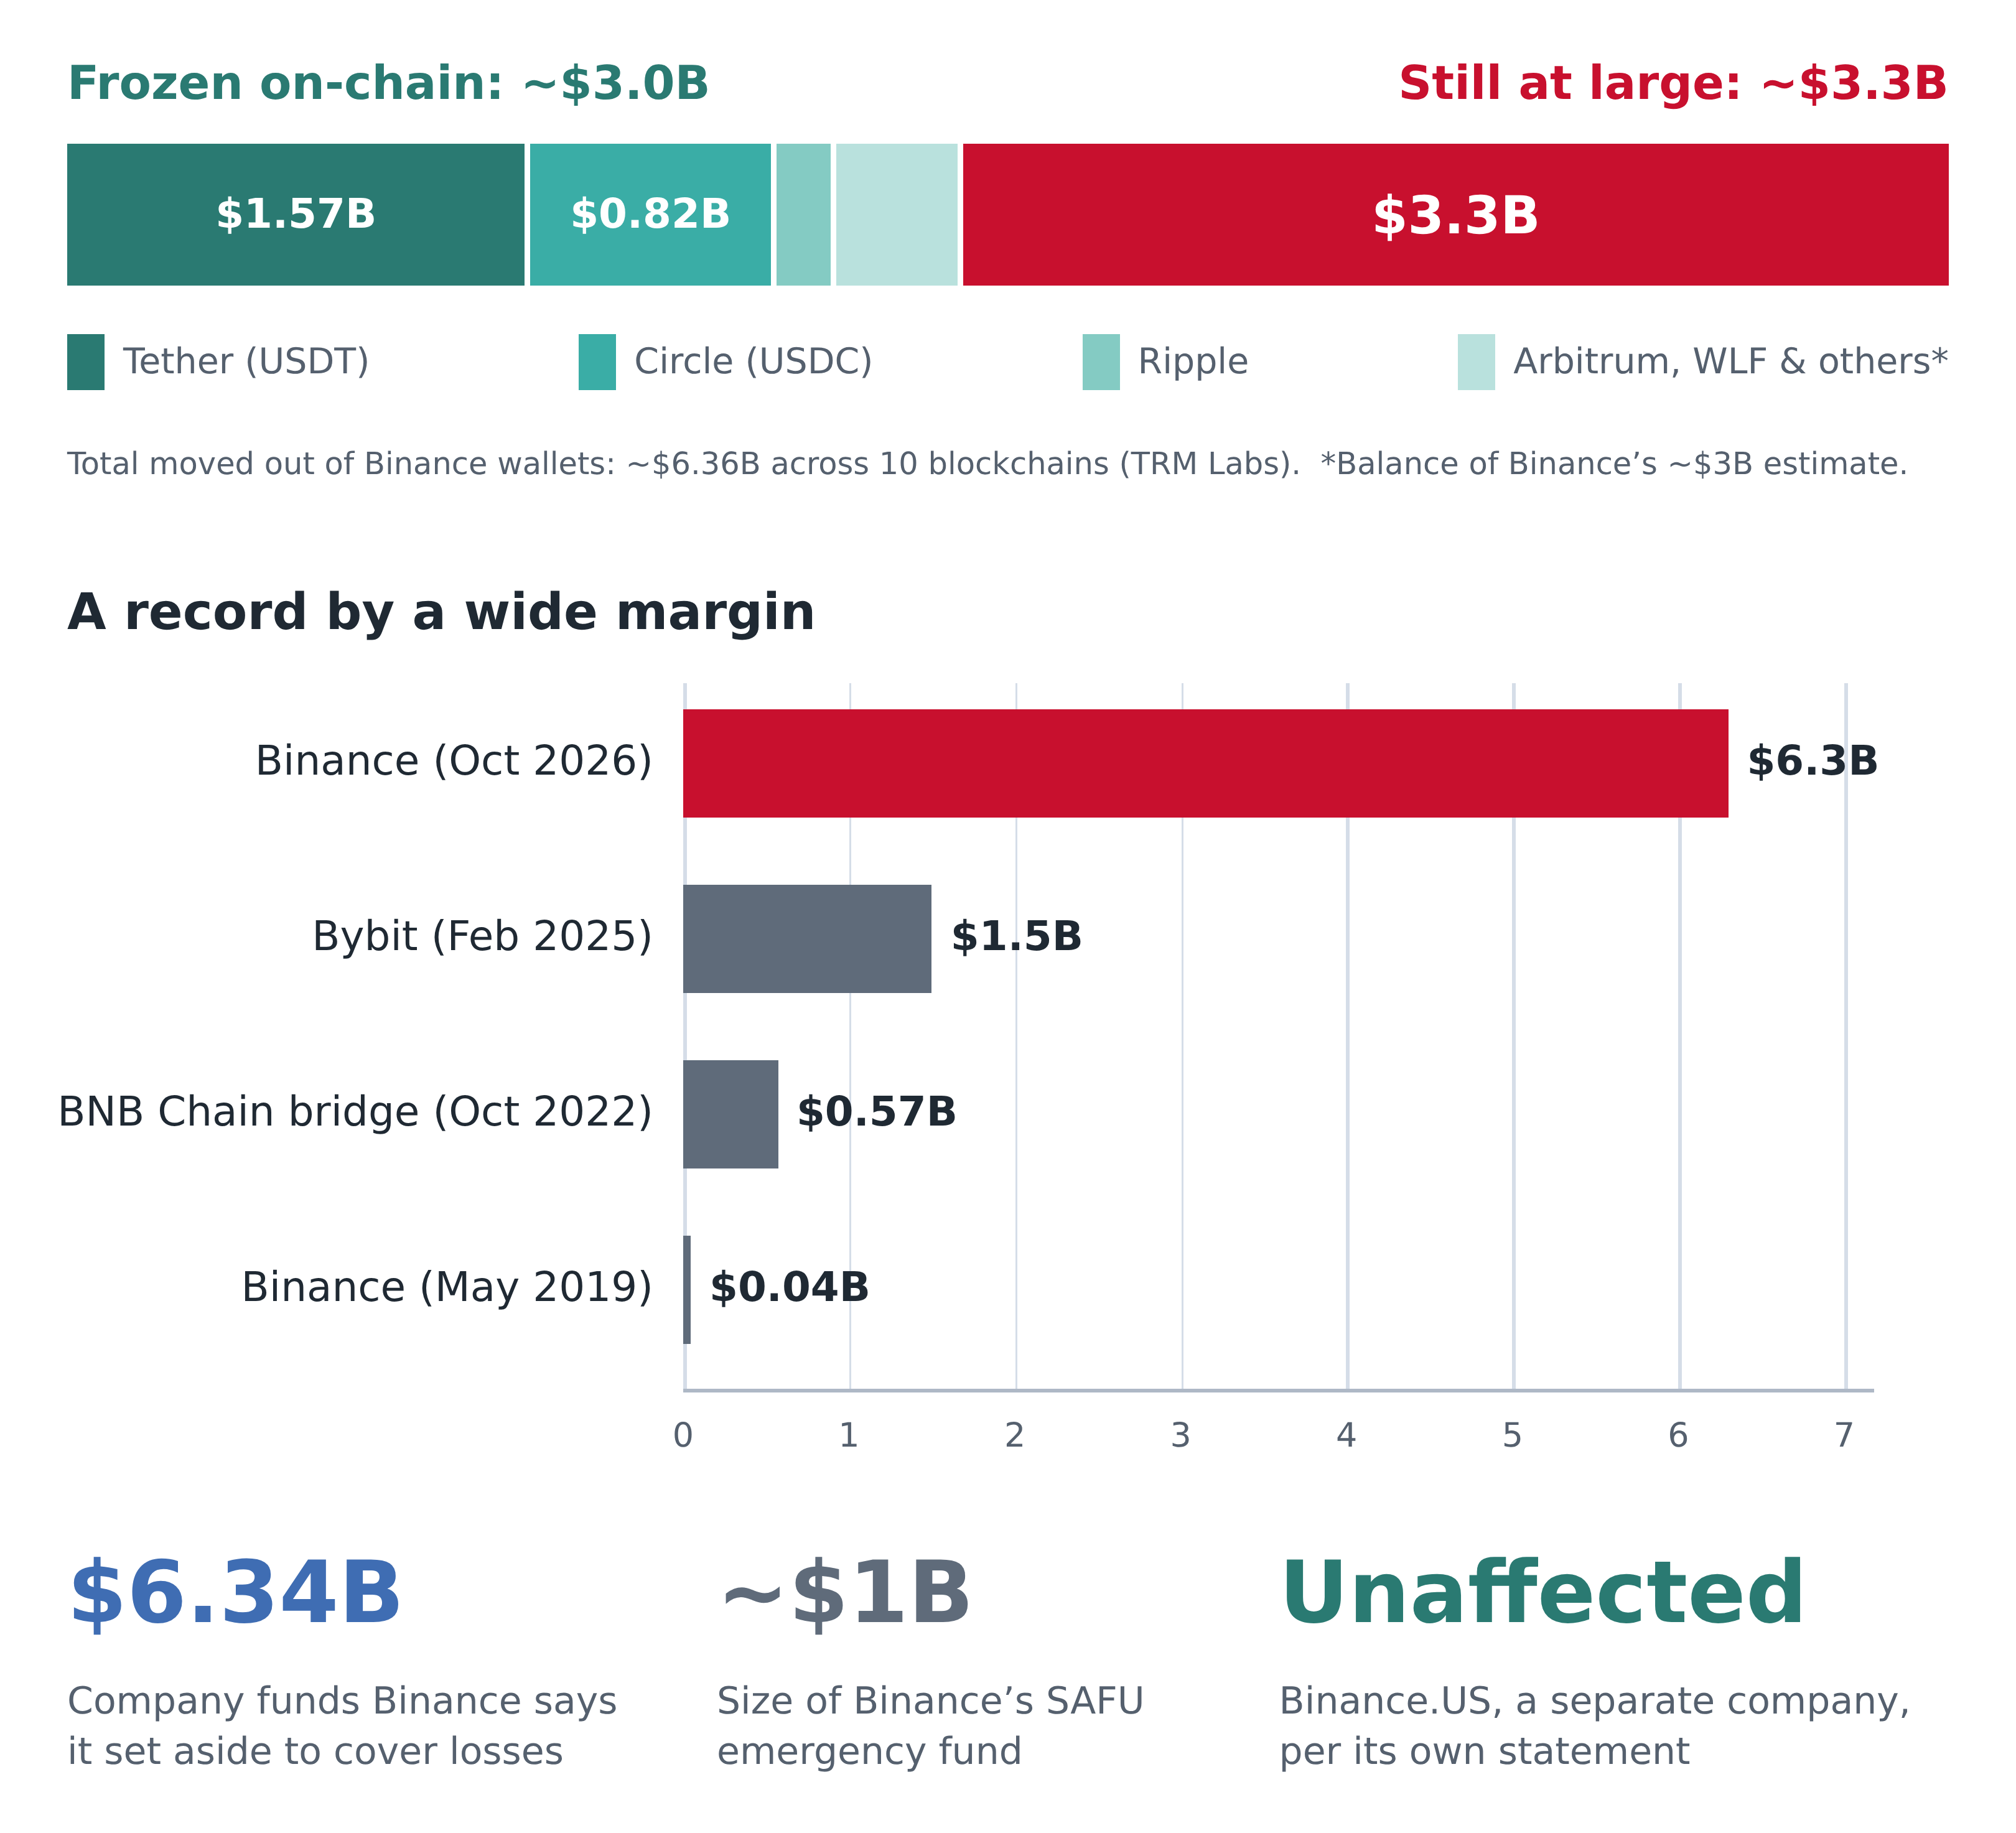
Infographic comparing the status and recovery of assets stolen in the Binance hack with losses from earlier major cryptocurrency exchange hacks, measured in billions of U.S. dollars. Shows reported asset freezes by issuers and Binance, noting that individual amounts may not total Binance’s estimated $3 billion in affected assets.

Figure 3. Status of the stolen assets and comparison with earlier major exchange hacks, in billions of U.S. dollars. Freeze amounts are as reported by issuers and Binance and do not sum precisely to Binance’s ~$3 billion estimate. Jeremy Swenson. Data from Binance, Tether, Circle, Reuters, Elliptic, TRM Labs (via CNBC), Al Jazeera, and Ynet News.[33] October 2026.

Were Customer Funds Stolen?

Binance maintains that customers will not lose money. Teng has said the incident was confined to the exchange’s own hot wallets and that customer assets are managed under a separate security system; Binance says it has secured more than $6.34 billion of company funds to cover the losses in full.[34] That sum is more than six times the size of Binance’s roughly $1 billion Secure Asset Fund for Users (SAFU), the emergency reserve created in 2018 for exactly this kind of event.[35] The company has not detailed where the additional funds came from, but it plans to publish a full proof-of-reserves report by November 2.[36]

In the near term, customers are feeling the effects through access rather than balances. Withdrawals remain suspended while Binance rebuilds its withdrawal system, and the company expects to restore them by Sunday, November 1.[37] Early messaging was also inconsistent: Binance insisted that user funds were completely safe while simultaneously pledging to cover all losses, a combination that understandably confused users.[38] Analysts at Fundstrat Global Advisors say the breach does not currently appear to pose a meaningful solvency risk to an exchange that reported about $162.8 billion in assets under custody and 335 million registered users as of its 2025 annual report.[39]

What About Binance.US?

Binance.US, which operates as a separate company, has said it was not affected, and Coinbase likewise reported no impact on its operations.[40] The one caveat concerns Americans who access the global Binance exchange in spite of its geographic restrictions, for example through a virtual private network; they are in the same withdrawal queue as every other global user.[41]

Market Impact

The hack struck an already fragile market. Bitcoin fell toward $77,000, ether dropped by nearly 6 percent, and Binance’s native BNB token slid by nearly 10 percent.[42] The market maker GSR reported that bid–ask spreads on spot bitcoin at Binance were about five times wider than normal early Friday, a sign of thin liquidity as traders pulled back.[43]

Six Takeaways for Leaders

1. The most privileged endpoints are the biggest attack surface. A single engineer’s laptop appears to have provided an early foothold into systems controlling billions of dollars. Developer and DevOps endpoints deserve the same scrutiny as production infrastructure.

2. Key security is not the same as signing security. Even if no private keys leaked, an attacker who can push transactions through a legitimate signing pipeline can do enormous damage. Authorization logic, withdrawal limits, and anomaly detection along the signing path matter as much as key custody.

3. Centralized controls cut both ways. The ability of Tether, Circle, and others to freeze roughly $3 billion is the main reason this was not a total loss. It is also a reminder that stablecoins carry issuer-level control: a feature in a crisis and a policy debate the rest of the time.

4. Counterparty risk is real, even at the top. If the world’s largest exchange can be breached, institutions and individuals alike should know where their assets sit, who holds the keys, and what happens contractually when something goes wrong.

5. Expect regulation to follow. Industry voices, including the head of Franklin Templeton’s crypto business, are already calling for stronger cybersecurity rules.[44] A theft of this scale gives policymakers fresh momentum on custody standards, proof-of-reserves requirements, and mandatory incident disclosure.

6. Defenses must operate at machine speed. An attack that drained billions in about twenty minutes and erased its own traces leaves no room for manual review. Automated withdrawal circuit breakers, real-time anomaly response, and preserved forensic logs are now baseline controls. With AI-enabled North Korean applicants flooding hiring pipelines, identity verification during recruiting also belongs inside the security perimeter.

The Bottom Line

Binance appears to have the balance sheet to absorb this loss, and a coordinated industry response froze nearly half of the stolen funds within hours. Yet the largest crypto theft in history occurred at the platform best resourced to prevent it. The forthcoming post-mortem will be one of the most important security documents the industry has produced, and it deserves close reading.

How is your organization thinking about custody and counterparty risk after this week? I would welcome your perspective in the comments.

About The Author

Jeremy A. Swenson is a disruptive-thinking security entrepreneur, futurist/researcher, and seasoned senior management technology risk and digital strategy consultant. His experience spans healthcare, retail, financial services, high technology, and government. He is a frequent speaker and published writer, and he also does some pro bono consulting in these areas. He holds a certificate in Media Technology Policy from Oxford University’s Media Policy Summer Institute, an MSST (Master of Science in Security Technologies) degree from the University of Minnesota’s Technological Leadership Institute (TLI), an MBA from Saint Mary’s University of Minnesota, and a BA in political science from the University of Wisconsin Eau Claire. He is an alum of the Federal Reserve Secure Payment Task Force, the Crystal, Robbinsdale, and New Hope Community Police Academy (MN), as well as the Minneapolis FBI Citizens Academy. You can follow him on LinkedIn and Twitter. You can contact him for speaking, media, or consulting engagements via his website here: https://jeremy-swenson.com/

Endnotes


[1]Ravie Lakshmanan, “Binance Suffers Security Breach Affecting $6.3 Billion in Assets, Nearly $3 Billion Frozen,” The Hacker News, October 30, 2026, accessed October 30, 2026, https://thehackernews.com/2026/10/binance-suffers-security-breach.html; “Binance Hit by Record $6.3 Billion Crypto Hack: ‘This Was a Complex Attack,’ Says Co-CEO,” Yahoo Finance, October 30, 2026, accessed October 30, 2026, https://finance.yahoo.com/markets/article/bitcoin-drops-to-76000-as-binance-hack-spooks-investors-tether-circle-freeze-assets-083406383.html.

[2]“Binance Hack: How CZ, Coinbase, Tether and 70+ Crypto Leaders Reacted to the $6.3B Theft,” Crypto Times, October 30, 2026, accessed October 30, 2026, https://www.cryptotimes.io/2026/10/30/binance-hack-how-cz-coinbase-tether-and-70-crypto-leaders-reacted-to-the-6-3b-theft/; “Binance Pauses Withdrawals as Hackers Suspected of Stealing Billions in Crypto,” TechCrunch, October 29, 2026, accessed October 30, 2026, https://techcrunch.com/2026/10/29/binance-pauses-withdrawals-as-hackers-suspected-of-stealing-billions-in-crypto/.

[3]“Binance’s $6.3 Billion Hack: What We Know and What Comes Next,” CNBC, October 30, 2026, accessed October 30, 2026, https://www.cnbc.com/2026/10/30/billions-in-crypto-frozen-in-binance-hack-heres-what-happens-next-.html.

[4]“Binance Targeted in $6.3 Billion Crypto Heist, the Largest Ever,” NBC News, October 29, 2026, updated October 29, 2026, accessed October 30, 2026, https://www.nbcnews.com/business/markets/binance-hack-tether-circle-stablecoins-rcna606445.

[5]Timeline compiled from “Binance Hack: How CZ, Coinbase, Tether and 70+ Crypto Leaders Reacted”; “Binance Hack Update: $6.3B Impact, $3B Frozen After DevOps Laptop Breach,” Crypto Times, October 30, 2026, accessed October 30, 2026, https://www.cryptotimes.io/2026/10/30/binance-hack-6-3b-impact-3b-frozen-after-devops-laptop-breach/; “Binance Hack: What We Know About the $6.3B Breach,” HackenProof (blog), October 30, 2026, accessed October 30, 2026, https://hackenproof.com/blog/binance-hack, which also reports the Arbitrum Security Council freeze; and “Binance CEO Says Full Proof-of-Reserves Report Due Nov. 2, Pledges Full Compensation for Hack Losses,” Bloomingbit, October 30, 2026, accessed October 30, 2026, https://en.bloomingbit.io/feed/news/123309. Binance statements as reported in Lakshmanan, “Binance Suffers Security Breach”; Tether’s as reported in “Binance Targeted in $6.3 Billion Crypto Heist”; and Circle’s as reported in “Binance Hit by $6.3 Billion Theft in What Could Be the Biggest Crypto Heist on Record,” Help Net Security, October 30, 2026, accessed October 30, 2026, https://www.helpnetsecurity.com/2026/10/30/binance-crypto-hack/.

[6]Lakshmanan, “Binance Suffers Security Breach.”

[7]Agence France-Presse, “Crypto Platform Binance Confirms ‘Complex’ $6.3 bn Hack,” Yahoo Finance, October 30, 2026, accessed October 30, 2026, https://finance.yahoo.com/markets/crypto/articles/crypto-platform-binance-confirms-major-013059975.html; “What We Know About the $6.3B Breach.”

[8]“Binance Hack: Teng Says No Private Key Leaked, and Blockaid Says Eleven Binance Keys Signed the Transfers,” FinanceFeeds, October 30, 2026, accessed October 30, 2026, https://financefeeds.com/binance-hack-eleven-keys-signed-no-leak/.

[9]Sam Sabin, “How North Korea Perfected the Crypto Heist,” Axios, October 31, 2026, accessed October 31, 2026, https://www.axios.com/2026/10/31/north-korea-hackers-binance-crypto.

[10]“Teng Says No Private Key Leaked.”

[11]“Binance Hit by $6.3 Billion Theft.”

[12]Sabin, “How North Korea Perfected the Crypto Heist.”

[13]Sabin, “How North Korea Perfected the Crypto Heist.”

[14]Sabin, “How North Korea Perfected the Crypto Heist.”

[15]“Binance Hack: What the $6.3 Billion Theft Means for US Crypto Users,” BreezyScroll, October 30, 2026, accessed October 30, 2026, https://www.breezyscroll.com/money/binance-hack-crypto-assets-frozen.

[16]“What We Know and What Comes Next.”

[17]Sabin, “How North Korea Perfected the Crypto Heist.”

[18]Elliptic, “The Largest Theft in History: North Korea Likely Behind the $6.4 Billion Binance Hack,” Elliptic Insights, October 30, 2026, accessed October 30, 2026, https://www.elliptic.co/insights/binance-largest-hack-in-history/.

[19]Reuters, “Hackers Steal $6.3 Billion from Binance in Record Heist Blamed on North Korea,” Yahoo Finance, October 30, 2026, accessed October 30, 2026, https://finance.yahoo.com/markets/crypto/articles/tether-circle-freeze-2-38-222607515.html.

[20]Sabin, “How North Korea Perfected the Crypto Heist.”

[21]Sabin, “How North Korea Perfected the Crypto Heist.”

[22]Sabin, “How North Korea Perfected the Crypto Heist.”

[23]Sabin, “How North Korea Perfected the Crypto Heist.”

[24]Sabin, “How North Korea Perfected the Crypto Heist.”

[25]“Binance Hit by $6.3 Billion Theft.”

[26]“Binance Targeted in $6.3 Billion Crypto Heist.”

[27]“Binance Hit by $6.3 Billion Theft.”

[28]Reuters, “Hackers Steal $6.3 Billion from Binance.”

[29]“What We Know About the $6.3B Breach.”

[30]Elliptic, “Largest Theft in History.”

[31]“Binance Says $6.3bn Stolen in Biggest Crypto Heist in History: What We Know,” Al Jazeera, October 30, 2026, accessed October 30, 2026, https://www.aljazeera.com/news/2026/10/30/binance-says-6-3bn-stolen-in-biggest-crypto-heist-in-history-what-we-know.

[32]Sabin, “How North Korea Perfected the Crypto Heist.”

[33]Total stolen and Binance’s frozen-funds estimate from Lakshmanan, “Binance Suffers Security Breach”; Tether freeze from “Binance Targeted in $6.3 Billion Crypto Heist”; Circle freeze from “Binance Hit by $6.3 Billion Theft”; Ripple freeze from Reuters, “Hackers Steal $6.3 Billion from Binance”; stablecoin and verified-frozen totals from Elliptic, “Largest Theft in History”; TRM Labs estimate from “What We Know and What Comes Next”; unaccounted-for remainder and earlier-hack comparison from “Binance Says $6.3bn Stolen”; and “Binance Reports $6.3 Billion Crypto Breach, Potentially the Biggest Hack in History,” Ynet News, October 30, 2026, accessed October 30, 2026, https://www.ynetnews.com/business/article/bjmb5f11tme.

[34]“Binance CEO Says Full Proof-of-Reserves Report Due Nov. 2.”

[35]“Binance Says $6.3bn Stolen.”

[36]Reuters, “Hackers Steal $6.3 Billion from Binance.” “Binance CEO Says Full Proof-of-Reserves Report Due Nov. 2.”

[37]“Binance CEO Says Full Proof-of-Reserves Report Due Nov. 2.”

[38]Agence France-Presse, “Binance Confirms ‘Complex’ $6.3 bn Hack.”

[39]“What We Know and What Comes Next.” Reuters, “Hackers Steal $6.3 Billion from Binance.”

[40]“Binance Reports $6.3 Billion Crypto Breach”; “Binance Hack Update.”

[41]“What the $6.3 Billion Theft Means for US Crypto Users.”

[42]“Live Updates: Bitcoin Falls to $77,000 as Binance Exploit Combines with Tech Woes,” CoinDesk, October 30, 2026, accessed October 30, 2026, https://www.coindesk.com/markets/2026/10/30/live-news-binance-hack-rattles-crypto-as-intel-plunges-and-ai-spending-fears-hit-tech; Agence France-Presse, “Binance Confirms ‘Complex’ $6.3 bn Hack.”

[43]Reuters, “Analysts React as Binance Freezes Assets after $6.3 Billion Security Breach,” Euronext Financial News, October 30, 2026, accessed October 30, 2026, https://live.euronext.com/en/financial-news/analysts-react-binance-freezes-assets-after-63-billion-security-breach.

[44]Chris Perkins, “Binance Hack Reveals Need for Stronger Cybersecurity Regulation,” interview, CNBC, video, October 30, 2026, accessed October 30, 2026, https://www.cnbc.com/video/2026/10/30/binance-hack-calls-for-stronger-cybersecurity-regulation-perkins.html.

AT&T Faces Massive Data Breach Impacting 73 Million and Negligence Lawsuits

Fig 1. AT&T Data Breach Infographic, WLBT3, 2024.

After weeks of denials, AT&T Inc. (NYSE:T), a leading player in the telecommunications sector, has recently unveiled a substantial data breach originating from 2019, leading to the compromise of sensitive information belonging to 73 million users [1]. This data breach has since surfaced on the dark web, exposing a trove of personal data including Social Security numbers, email addresses, phone numbers, and dates of birth, impacting both current and past account holders. The compromised information encompasses names, addresses, phone numbers, and for numerous individuals, highly sensitive data such as Social Security numbers, dates of birth, and AT&T passcodes.

How can you determine if you were impacted by the AT&T data breach? Firstly, ask yourself if you ever were a customer, and do not rely solely on AT&T to notify you. By utilizing services like Have I Been Pwned, you can ascertain if your data has been compromised. Additionally, Google’s Password Checkup tool can notify you if your account details are exposed, especially if you store password information in a Google account. For enhanced security, the premium edition of Bitwarden, a top-rated recommended password manager, offers the capability to scan for compromised passwords across the internet.

One prevalent issue concerning data breaches is the tendency for individuals to overlook safeguarding their data until it’s too late. It’s a common scenario – we often don’t anticipate our personal information falling into the hands of hackers who then sell it to malicious entities online. Regrettably, given the frequency and magnitude of cyber-attacks, the likelihood of your data being exposed has shifted from an “if” to a “when” scenario.

Given this reality, it’s imperative to adopt measures to safeguard your identity and data online, including [2]:

  1. Implementing multi-factor authentication – a crucial step in thwarting hackers’ attempts to infiltrate your accounts, even if your email address is publicly available.
  2. Avoiding password reuse and promptly changing passwords if they are compromised in a data breach – this practice ensures that even if your login credentials are exposed, hackers cannot infiltrate other accounts you utilize, including the one that has experienced a breach.
  3. Investing in identity protection services, either as standalone solutions or as part of comprehensive internet security suites – identity protection software can actively monitor the web for data breaches involving you, enabling you to take proactive measures to safeguard your identity.

AT&T defines a customer’s passcode as a numeric Personal Identification Number (PIN), typically consisting of four digits. Distinguishing it from a password, a passcode is necessary for finalizing an AT&T installation, conducting personal account activities over the phone, or reaching out to technical support, according to AT&T.

How to reset your AT&T passcode:

AT&T has taken steps to reset passcodes for active accounts affected by the data breach. However, as a precautionary measure, AT&T advises users who haven’t altered their passcodes within the last year to do so. Below are the steps to change your AT&T passcode:

  1. Navigate to your myAT&T Profile.
  2. Sign in when prompted. (If additional security measures are in place and sign-in isn’t possible, AT&T suggests opting for “Get a new passcode.”)
  3. Locate “My linked accounts” and select “Edit” for the passcode you wish to update.
  4. Follow the provided prompts to complete the process.

Here is AT&T’s official statement on the matter from 03/03/24 [3]:

“Based on our preliminary analysis, the data set appears to be from 2019 or earlier, impacting approximately 7.6 million current AT&T account holders and approximately 65.4 million former account holders. Currently, AT&T does not have evidence of unauthorized access to its systems resulting in exfiltration of the data set. The company is communicating proactively with those impacted and will be offering credit monitoring at our expense where applicable. We encourage current and former customers with questions to visit http://www.att.com/accountsafety for more information.”

The hackers behind this, allegedly ShiningHacker, endeavored to profit from the pilfered data by listing it for sale on the RaidForums data theft forum, initiating the bidding at $200,000 and entertaining additional offers in increments of $30,000 [4]. Moreover, they demonstrated readiness to promptly sell the data for $1 million, highlighting the gravity and boldness of the cyber offense.

Not surprisingly, AT&T is currently confronting numerous class-action lawsuits subsequent to the company’s acknowledgment of this data breach, which compromised the sensitive information of 73 million existing and former customers [5]. Among the ten lawsuits filed, one is being handled by Morgan & Morgan, representing plaintiff Patricia Dean and individuals in similar circumstances.

The lawsuit levels allegations of negligence, breach of implied contract, and unjust enrichment against AT&T, contending that the company’s deficient security measures and failure to promptly provide adequate notification about the data breach exposed customers to significant risks, including identity theft and various forms of fraud. It seeks compensatory damages, restitution, injunctive relief, enhancements to AT&T’s data security protocols, future audits, credit monitoring services funded by the company, and a trial by jury [6].


About the Author:

Jeremy Swenson is a disruptive-thinking security entrepreneur, futurist/researcher, and senior management tech risk consultant. He is a frequent speaker, published writer, podcaster, and even does some pro bono consulting in these areas. He holds an MBA from St. Mary’s University of MN, an MSST (Master of Science in Security Technologies) degree from the University of Minnesota, and a BA in political science from the University of Wisconsin Eau Claire. He is an alum of the Federal Reserve Secure Payment Task Force, the Crystal, Robbinsdale and New Hope Citizens Police Academy, and the Minneapolis FBI Citizens Academy.

References:


[1] AT&T. “AT&T Addresses Recent Data Set Released on the Dark Web.” 03/30/24: https://about.att.com/story/2024/addressing-data-set-released-on-dark-web.html

[2] Colby, Clifford, Combs, Mary-Elisabeth; “Data From 73 Million AT&T Accounts Stolen: How You Can Protect Yourself.” CNET. 04/02/24: https://www.cnet.com/tech/mobile/data-from-73-million-at-t-accounts-stolen-how-you-can-protect-yourself/

[3] AT&T. “AT&T Addresses Recent Data Set Released on the Dark Web.” 03/30/24: https://about.att.com/story/2024/addressing-data-set-released-on-dark-web.html

[4] Naysmith, Caleb. “73 Million AT&T Users’ Data Leaked As Hacker Said, ‘I Don’t Care If They Don’t Admit. I’m Just Selling’ Auctioned At Starting Price Of $200K”. https://finance.yahoo.com/news/73-million-t-users-data-173015617.html

[5] Kan, Michael. “AT&T Faces Class-Action Lawsuit Over Leak of Data on 73M Customers.” PC Mag. 04/02/24: https://www.pcmag.com/news/att-faces-class-action-lawsuit-over-leak-of-data-on-73m-customers

[6] Kan, Michael. “AT&T Faces Class-Action Lawsuit Over Leak of Data on 73M Customers.” PC Mag. 04/02/24: https://www.pcmag.com/news/att-faces-class-action-lawsuit-over-leak-of-data-on-73m-customers

Top 16 Ways SMBs Can Mitigate Cyber Risks and Threats.

Fig. 1. Stock Cyber Brain Graphic, 2022.
  1. Sign up for DHS CISA e-mail alerts specific to your company and industry needs and review the alerts:
    1. Sign up here.
    2. Use the free DHS developed CSET (Cybersecurity Evaluation Tool) to assess your security posture – High, Med, or Low. CSET is downloadable here.
  2. Educate Employees About Cyber Threats and Hold Them Accountable:
    1. Educate your employees about online threats and how to protect your business’s data, including safe use of social networking sites. Depending on the nature of your business, employees might be introducing competitors to sensitive details about your firm’s internal business.
    2. Employees should be informed about how to post online in a way that does not reveal any trade secrets to the public or competing businesses. 
    3. Use games with training and hold everyone accountable to security policies and procedures.
    4. This needs to be embedded in the culture of your company.
    5. Register for free DHS cyber training here.
    6. Use the free DHS SMB cyber resource toolkit.
  3. Protect Against Viruses, Spyware, and Other Malicious Code:
    1. Make sure each of your business’s computers are equipped with antivirus software and antispyware and updated regularly. Such software is readily available online from a variety of vendors. All software vendors regularly provide patches and updates to their products to correct security problems and improve functionality. Configure all software to install updates automatically. Especially watch freeware which contains malvertising.
  4. Secure Your Networks:
    1. Safeguard your Internet connection by using a firewall and encrypting information. If you have a Wi-Fi network, make sure it is secure and hidden. To hide your Wi-Fi network, set up your wireless access point or router so it does not broadcast the network name, known as the Service Set Identifier (SSID).
    2. Have a secure strong password to protect access to the router (xeeityyg18695845%&*&RELxu78IGO) — example.
    3. Lastly, use a VPN (virtual private network).
  5. Control Physical Access to Computers and Network Components:
    1. Prevent access or use of business computers by unauthorized individuals. Laptops can be particularly easy targets for theft or can be lost, so lock them up when unattended. Make sure a separate user account is created for each employee and require strong passwords.
    2. Administrative privileges should only be given to trusted IT staff and key personnel.
  6. Create A Mobile Device Protection Plan:
    1. Require users to password-protect their devices, encrypt their data, and install security apps to prevent criminals from stealing information while the phone is on public networks.
    2. Use a containerization application to separate personal data from company data.
    3. Be sure to set reporting procedures for lost or stolen equipment.
  7. Protect All Pages on Your Public-Facing Webpages, Not Just the Checkout and Sign-Up Pages:
    1. Make sure submission forms can block spam and can block code execution (cross-side scripting attacks).
  8. Establish Security Practices and Policies to Protect Sensitive Information:
    1. Establish policies on how employees should handle and protect personally identifiable information and other sensitive data. Clearly outline the consequences of violating your business’s cybersecurity policies and who is accountable.
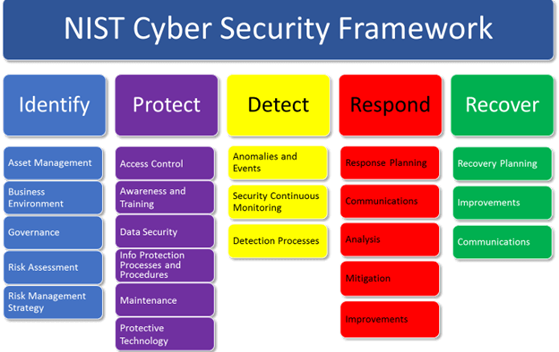
  9. Base Your Security Strategy Significantly on the NIST Cybersecurity Framework 1.1: Identify, Detect Defend, Respond, and Recover:
    1. The NIST Cybersecurity Framework Small Business Resources are linked here.
No alt text provided for this image
Fig. 2. NIST Cyber Security Framework Sub Tasks, NIST, 2022:
  1. Require Employees to Use Strong Passwords and to Change Them Often:
    1. Consider implementing multifactor authentication that requires additional information beyond a password to gain entry. Check with your vendors that handle sensitive data, especially financial institutions, to see if they offer multifactor authentication for your account. Smart card plus passcode for example.
  2. Employ Best Practices on Payment Cards:
    1. Work with your banks or card processors to ensure the most trusted and validated tools and anti-fraud services are being used. You may also have additional security obligations related to agreements with your bank or processor. Isolate payment systems from other, less secure programs and do not use the same computer to process payments and surf the Internet. 
    2. Outsource some or all of it and know where your risk responsibility ends.
  3. Make Backup Copies of Important Business Data and Use Encryption When Possible:
    1. Regularly backup the data on all computers. Critical data includes word processing documents, electronic spreadsheets, databases, financial files, human resources files, and accounts receivable/payable files. Backup data automatically if possible, or at least weekly, and store the copies either offsite or on the cloud. 
    2. Having all key files backed up via the 3-2-1 rule — three copies of files in two different media forms with one offsite — thus reducing ransomware attack damage.
  4.  Make Sure Your Vendors Have the Required Security Compliance Attestations and Insurance:
    1. SOC 2, PCI, and HIPAA for example.
    2. Cyber/data breach insurance should be separate from general business liability, and you should know the exclusions and sub-limits.
  5. Use A Password Management Tool and Strong Passwords:
    1. Another way to stay safe is by setting passwords that are longer, complex, and thus hard to guess. Additionally, they can be stored and encrypted for safekeeping using a well-regarded password vault and management tool. This tool can also help you to set strong passwords and can auto-fill them with each login — if you select that option. Yet using just the password vaulting tool is all that is recommended. Doing these two things makes it difficult for hackers to steal passwords or access your accounts.
  6. Use Only Whitelisted Sites Not Blacklisted Ones or Ones Found Via the Dark Web:
    1. Use only approved whitelisted platforms and sites that do not expose you to data leakages or intrusion on your privacy. Whitelisting is the practice of explicitly allowing some identified websites access to a particular privilege, service, or access. Backlisting is blocking certain sites or privileges. If a site does not assure your privacy, do not even sign up let alone participate.
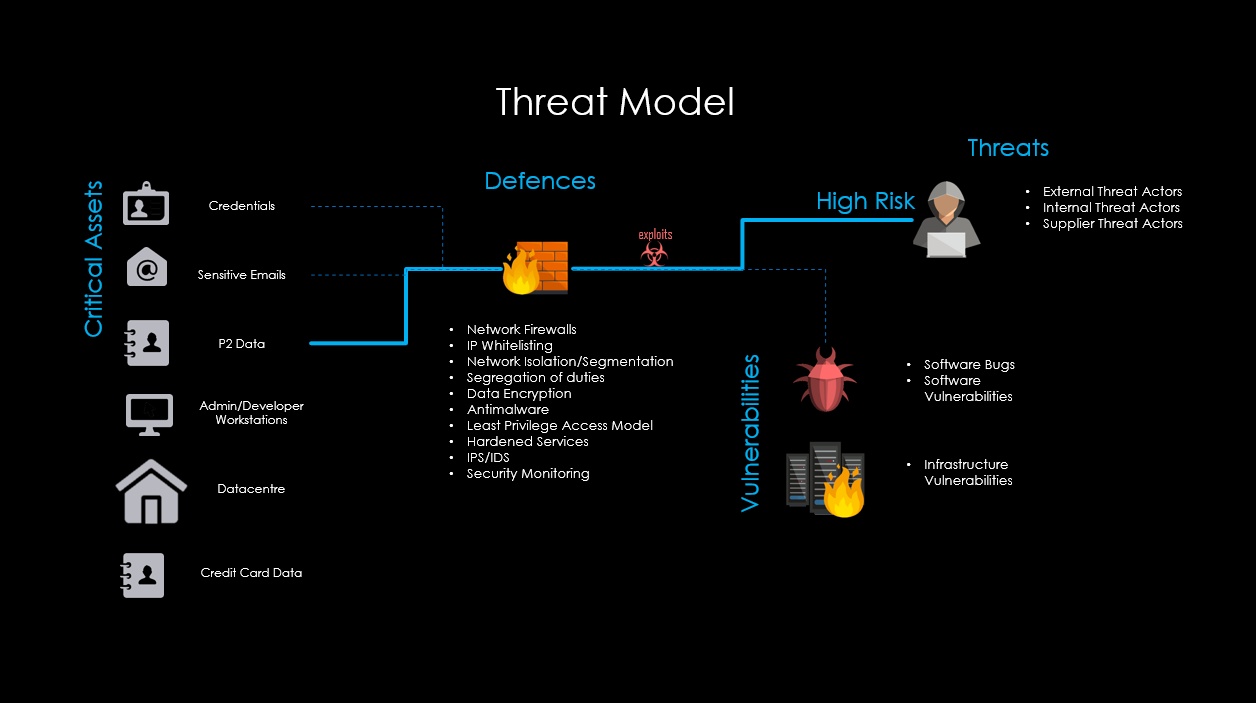
  7. Mimic Your Likely Threats with a Threat Modeling Methodology that works for your Industry:
    1. PASTA, VAST, and FAIR are just a few.

Five Cyber-Tech Trends of 2021 and What it Means for 2022.

Minneapolis — 01/08/22

By Jeremy Swenson

Intro:

Every year I like to research and commentate on the most impactful security technology and business happenings from the prior year. This year is unique since the pandemic and mass resignation/gig economy continues to be a large part of the catalyst for most of these trends. All these trends are likely to significantly impact small businesses, government, education, high tech, and large enterprise in big and small ways.

Fig. 1. Facebook Whistle Blower and Disinformation Mashup (Getty & Stock Mashup, 2021).

Summary:

The pandemic continues to be a big part of the catalyst for digital transformation in tech automation, identity and access management (IAM), big data, collaboration tools, artificial intelligence (AI), and increasingly the supply chain. Disinformation efforts morphed and grew last year challenging data and culture. This requires us to put more attention on knowing and monitoring our own social media baselines. We no longer have the same office due to mass work from home (WFH) and the mass resignation/gig economy. This infers increased automated zero-trust policies and tools for IAM with less physical badge access required. The security perimeter is now more defined by data analytics than physical/digital boundaries.

The importance of supply chain cyber security was elevated by the Biden Administration’s Executive Order 1407 in response to hacks including SolarWinds and Colonial Pipeline. Education and awareness around the review and removal of non-essential mobile apps grows as a top priority as mobile apps multiply. All the while, data breaches, and ransomware reach an all-time high while costing more to mitigate.

1) Disinformation Efforts Accelerate Challenging Data and Culture:

Disinformation has not slowed down any in 2021 due to sustained advancements in communications technologies, the growth of large social media networks, and the “appification” of everything thereby increasing the ease and capability of disinformation. Disinformation is defined as incorrect information intended to mislead or disrupt, especially propaganda issued by a government organization to a rival power or the media. For example, governments creating digital hate mobs to smear key activists or journalists, suppress dissent, undermine political opponents, spread lies, and control public opinion (Shelly Banjo; Bloomberg, 05/18/2019).

Today’s disinformation war is largely digital via platforms like Facebook, Twitter, Instagram, Reddit, WhatsApp, Yelp, Tik-tok, SMS text messages, and many other lesser-known apps. Yet even state-sponsored and private news organizations are increasingly the weapon of choice, creating a false sense of validity. Undeniably, the battlefield is wherever many followers reside. 

Bots and botnets are often behind the spread of disinformation, complicating efforts to trace and stop it. Further complicating this phenomenon is the number of app-to-app permissions. For example, the CNN and Twitter apps having permission to post to Facebook and then Facebook having permission to post to WordPress and then WordPress posting to Reddit, or any combination like this. Not only does this make it hard to identify the chain of custody and original source, but it also weakens privacy and security due to the many authentication permissions involved. The copied data is duplicated at each of these layers which is an additional consideration.

We all know that false news spreads faster than real news most of the time, largely because it is sensationalized. Since most disinformation draws in viewers which drives clicks and ad revenues; it is a money-making machine. If you can significantly control what’s trending in the news and/or social media, it impacts how many people will believe it. This in turn impacts how many people will act on that belief, good or bad. This is exacerbated when combined with human bias or irrational emotion. For example, in late 2021 there were many cases of fake COVID-19 vaccines being offered in response to human fear (FDA; 09/28/2021). This negatively impacts culture by setting a misguided example of what is acceptable.

There were several widely reported cases of political disinformation in 2021 including misleading texts, e-mails, mailers, Facebook censorship, and robocalls designed to confuse American voters amid the already stressful pandemic. Like a narcissist’s triangulation trap, these disinformation bursts riled political opponents on both sides in all states creating miscommunication, ad hominin attacks, and even derailed careers with impacts into the future (PBS; The Hinkley Report, 11/24/20 and Daniel Funke; USA Today, 12/23/21).

Facebook is significantly involved in disinformation as one recent study stated, “Globally, Facebook made the wrong decision for 83 percent of those ads that had not been declared as political by their advertisers and that Facebook or the researchers deemed political. Facebook both overcounted and undercounted political ads in this group” (New York University; Cybersecurity For Democracy, 2021). Of course, Facebook disinformation whistleblower Frances Haugen who testified before Congress in 2021 is only more evidence of these and related Facebook failings. Specifically that “Facebook executives, including CEO Mark Zuckerberg, misstated and omitted key details about what was known about Facebook and Instagram’s ability to cause harm” (Bobby Allyn; NPR, 10/05/21).

Fig. 2. Facebook Gaps in Ad Transparency (IMEC-DistriNet KU Leuven and NYU Cyber Security for Democracy, 2021).

With the help of Facebook’s misinformation, huge swaths of confused voters and activists aligned more with speculation and emotion/hype than unbiased facts, and/or project themselves as fake commentators. This dirtied the data in terms of the election process and only begs the question – which parts of the election information process are broken? This normalizes petty policy fights, emotional reasoning, lack of unbiased intellectualism – negatively impacting western culture. All to the threat actor’s delight. Increased public to private partnerships, more educational rigor, and enhanced privacy protections for election and voter data are needed to combat this disinformation.

2) Identity and Access Management (IAM) Scrutiny Drives Zero Trust Orchestration:

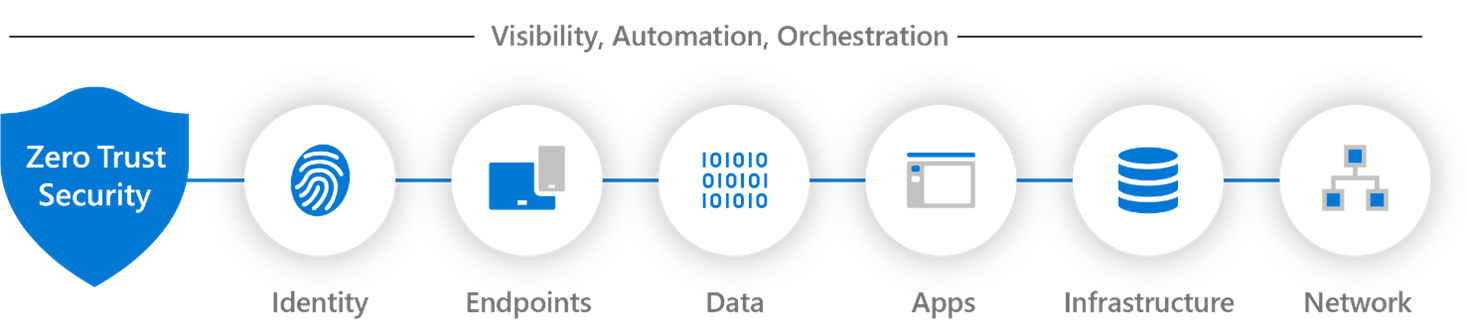
The pandemic and mass resignation/gig economy has pushed most organizations to amass work from home (WFH) posture. Generally, this improves productivity making it likely to become the new norm. Albeit with new rules and controls. To support this, 51% of business leaders started speeding up the deployment of zero trust capabilities in 2020 (Andrew Conway; Microsoft, 08/19/20) and there is no evidence to suggest this is slowing down in the next year but rather it is likely increasing to support zero trust orchestration. Orchestration is enhanced automation between partner zero trust applications and data, while leaving next to no blind spots. This reduces risk and increases visibility and infrastructure control in an agile way. The quantified benefit of deploying mature zero trust capabilities including orchestration is on average $ 1.76 million dollars less in breach response costs when compared to an organization who has not rolled out zero trust capabilities (IBM Security, Cost of A Data Breach Report, 2021). 

Fig. 3. Zero Trust Components to Orchestration (Microsoft, 09/17/21).

Zero trust moves organizations to a need-to-know-only access mindset with inherent deny rules, all the while assuming you are compromised. This infers single sign-on at the personal device level and improved multifactor authentication. It also infers better role-based access controls (RBAC), firewalled networks, improved need-to-know policies, effective whitelisting and blacking listing of apps, group membership reviews, and state of the art PAM (privileged access management) tools for the next year. In the future more of this is likely to better automate and orchestrate (Fig. 3.) zero trust abilities so that one part does not hinder another part via complexity fog.

3) Security Perimeter is Now More Defined by Data Analytics than Physical/Digital Boundaries:

This increased WFH posture blurs the security perimeter physically and digitally. New IP addresses, internet volume, routing, geolocation, and virtual machines (VMs) exacerbate this blur. This raises the criticality of good data analytics and dashboarding to define the digital boundaries in real-time. Therefore, prior audits, security controls, and policies may be ineffective. For instance, empty corporate offices are the physical byproduct of mass WFH, requiring organizations to set default disable for badge access. Extra security in or near server rooms is also required. The pandemic has also made vendor interactions more digital, so digital vendor connection points should be reduced and monitored in real-time, and the related exception policies should be re-evaluated.

New data lakes and machine learning informed patterns can better define security perimeter baselines. One example of this includes knowing what percent of your remote workforce is on what internet providers and what type? For example, Google fiber, Comcast cable, CenturyLink DSL, ATT 5G, etc. There are only certain modems that can go with each of these networks and that leaves a data trail. Of course, it could be any type of router. What type of device do they connect with MAC, Apple, VM, or other, and if it is healthy can all be determined in relationship to security perimeter analytics.

4) Supply Chain Risk and Attacks Increase Prompting Government Action:

Every organization has a supply chain big or small. There are even subcomponents of the supply chain that can be hard to see like third/fourth-party vendors. A supply chain attack works by targeting a third/fourth party with access to an organization’s systems instead of hacking their networks directly.

In 2021 cybercriminals focused their surveillance on key components of the supply chain including hacking DNS servers, switches, routers, VPN concentrators and services, and other supply chain connected components at the vendor level. Of note was the massive Colonial Gas Pipeline hack that spiked fuel prices this last summer. This was caused by one compromised VPN account informed by a leaked password from the dark web (Turton, William; and Mehrotra, Kartikay; Bloomberg, 06/04/21). The SolarWinds hack was another supply chain-originated attack in that they got into SolarWinds IT management product Orien which in turn got them into the networks of most of the customers of that product (Lily Hay Newman; Wired, 12/19/21). The research consensus unsurprisingly ties this attack to Russian affiliated threat actors and there is no evidence contracting that.

In response to these and related attacks the U.S. Presidential Administration issued Executive Order 14017, the heart of which requires those who manufacture and distribute software a new awareness of their supply chain to include what is in their products, even open-source software (White House; 05/12/21). This in addition to more spending on CISA hiring and public relations efforts for vulnerabilities and NIST framework conformance. Time will tell what this order delivers as it is dependent on what private sector players do.

Fig. 4. Supply Chain Cyber Attack Diagram (INSURETrust, 2021).

5) Data Breaches Have Greatly Increased in Number and Cost:

The pandemic has continued to be a part of the catalyst for increased lawlessness including fraud, ransomware, data theft, and other types of profitable hacking. Cybercriminals are more aggressively taking advantage of geopolitical conflict and legal standing gaps. For example, almost all hacking operations are in countries that do not have friendly geopolitical relations with the United States or its allies – and all their many proxy hops would stay consistent with this. These proxy hops are how they hide their true location and identity.

Moreover, with local police departments extremely overworked and understaffed with their number one priority being responding to the huge uptick in violent crime in most major cities, white-collar cybercrimes remain a low priority. Additionally, local police departments have few cyber response capabilities depending on the size of their precinct. Often, they must sheepishly defer to the FBI, CISA, and the Secret Service, or their delegates for help. Yet not unsurprisingly, there is a backlog for that as well with preference going to large companies of national concern that fall clearly into one of the 16 critical infrastructures. That is if turf fights and bureaucratic roadblocks don’t make things worse. Thus, many mid and small-sized businesses are left in the cold to fend for themselves which often results in them paying ransomware, and then being a victim a second time all the while their insurance carrier drops them.

Further complicating this is lack of clarity on data breach and business interruption insurance coverage and terms. Keep in mind most general business liability insurance policies and terms were drafted before hacking was invented so they are by default behind the technology. Most often general liability business insurance covers bodily injuries and property damage resulting from your products, services, or operations. Please see my related article 10 Things IT Executives Must Know About Cyber Insurance to understand incident response and to reduce the risk of inadequate coverage and/or claims denials.

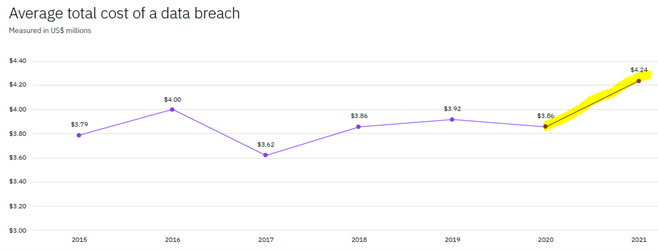
According to the Identity Theft Resource Center (ITRC)’s 2021Q3 Data Breach Report, there was a 17% year-over increase as of 09/30/21. This means that by the time they finish their Q4 2021 report it’s likely to be above a 30% year-over-year increase. Breaches are also more costly for organizations suffering them according to the IBM Security Cost of Data Breach Report (Fig 5).

Fig 5. Cost of A Data Breach Increases 2020 to 2021 (IBM Security, 2021).

From 2020 to 2021 the average cost of a data breach in U.S. dollars rose to $4.24 million from $3.86 million. This is almost a 10% increase at 9.1%. In contrast, the preceding 4 years were relatively flat (Fig 5). The pandemic and policing conundrum is a considerable part of this uptick.

Lastly, this is a lot of money for an organization to spend on a breach. Yet this amount could be higher when you factor in other long-term consequence costs such as increased risk of a second breach, brand damage, and/or delayed regulatory penalties that were below the surface – all of which differs by industry. In sum, it is cheaper and more risk prudent to spend even $4.24 million or a relative percentage at your organization on preventative zero trust capabilities than to deal with the cluster of a data breach.

Take-Aways:

COVID-19 remains a catalyst for digital transformation in tech automation, IAM, big data, collaboration tools, and AI. We no longer have the same office and thus less badge access is needed. The growth and acceptability of mass WFH combined with the mass resignation/gig economy remind employers that great pay and culture alone are not enough to keep top talent. Signing bonuses and personalized treatment are likely needed. Single sign-on (SSO) will expand to personal devices and smartphones/watches. Geolocation-based authentication is here to stay with double biometrics likely. The security perimeter is now more defined by data analytics than physical/digital boundaries, and we should dashboard this with machine learning and AI tools.

Education and awareness around the review and removal of non-essential mobile apps is a top priority. Especially for mobile devices used separately or jointly for work purposes. This requires a better understanding of geolocation, QR code scanning, couponing, digital signage, in-text ads, micropayments, Bluetooth, geofencing, e-readers, HTML5, etc. A bring your own device (BYOD) policy needs to be written, followed, and updated often informed by need-to-know and role-based access (RBAC) principles. Organizations should consider forming a mobile ecosystem security committee to make sure this unique risk is not overlooked or overly merged with traditional web/IT risk. Mapping the mobile ecosystem components in detail is a must.

IT and security professionals need to realize that alleviating disinformation is about security before politics. We should not be afraid to talk about it because if we are then our organizations will stay weak and insecure and we will be plied by the same political bias that we fear confronting. As security professionals, we are patriots and defenders of wherever we live and work. We need to know what our social media baseline is across platforms. More social media training is needed as many security professionals still think it is mostly an external marketing thing. Public-to-private partnerships need to improve and app to app permissions need to be scrutinized. Enhanced privacy protections for election and voter data are needed. Everyone does not need to be a journalist, but everyone can have the common sense to identify malware-inspired fake news. We must report undue bias in big tech from an IT, compliance, media, and a security perspective.

Cloud infra will continue to grow fast creating perimeter and compliance complexity/fog. Organizations should preconfigure cloud-scale options and spend more on cloud-trained staff. They should also make sure that they are selecting more than two or three cloud providers, all separate from one another. This helps staff get cross-trained on different cloud platforms and add-ons. It also mitigates risk and makes vendors bid more competitively. 

The increase in number and cost of data breaches was in part attributed to vulnerabilities in supply chains in a few national data breach incidents in 2021. Part of this was addressed in President Biden’s Executive Order 1407 on supply chain security. This reminds us to replace outdated routers, switches, repeaters, controllers, and to patch them immediately. It also reminds us to separate and limit network vendor access points to strictly what is needed and for a limited time window. Last but not least, we must have up-to-date thorough business interruption / cyber insurance with detailed knowledge of what it requires for incident response with breach vendors pre-selected.  

About the Author:

Jeremy Swenson is a disruptive thinking security entrepreneur, futurist/researcher, and senior management tech risk consultant. Over 17 years he has held progressive roles at many banks, insurance companies, retailers, healthcare orgs, and even governments including being a member of the Federal Reserve Secure Payment Task Force. Organizations relish in his ability to bridge gaps and flesh out hidden risk management solutions while at the same time improving processes. He is a frequent speaker, published writer, podcaster, and even does some pro bono consulting in these areas. As a futurist, his writings on digital currency, the Target data breach, and Google combining Google + video chat with Google Hangouts video chat have been validated by many. He holds an MBA from St. Mary’s University of MN, a MSST (Master of Science in Security Technologies) degree from the University of Minnesota, and a BA in political science from the University of Wisconsin Eau Claire.

Abstract Forward Podcast #10: CISO Risk Management and Threat Modeling Best Practices with Donald Malloy and Nathaniel Engelsen!

Fig. 1. Joe the IT Guy, 10/17/2018

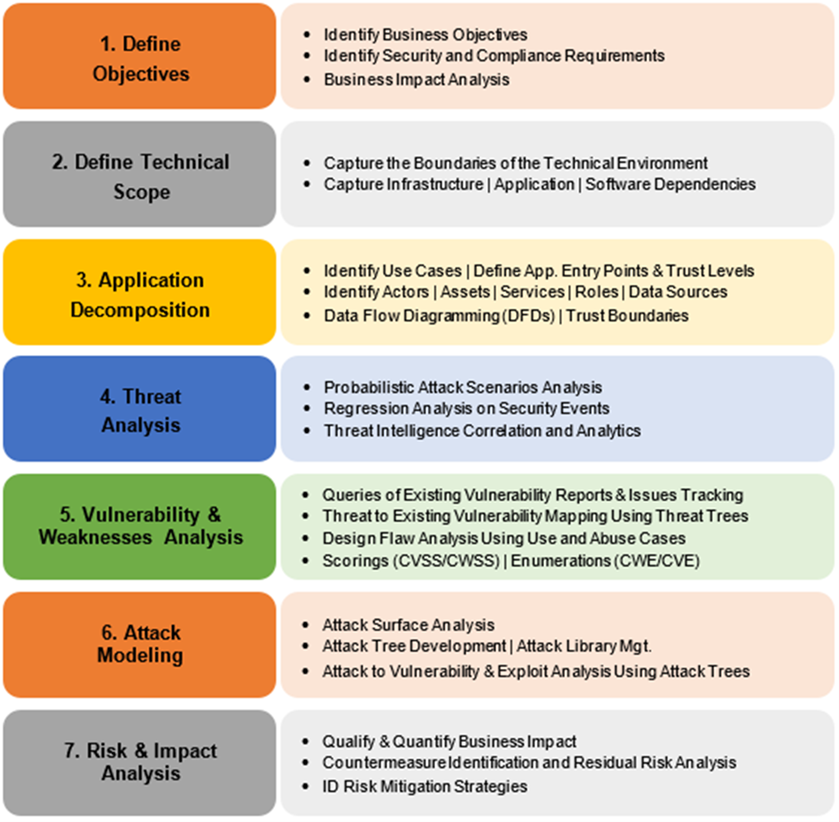
Featuring the esteemed technology and risk thought leaders Donald Malloy and Nathaniel Engelsen — this episode covers threat modeling methodologies STRIDE, Attack Tree, VAST, and PASTA. Specifically, how to apply them with limited budgets. It also discusses the complex intersection of how to derive ROI on threat modeling with compliance and insurance considerations. We then cover IAM best practices including group and role level policy and control best practices. Lastly, we hear a few great examples of key CISO risk management must-dos at the big and small company levels.

Fig. 2. Pasta Threat Modeling Steps (Nataliya Shevchenko, CMU, 12/03/2018).

Donald Malloy has more than 25 years of experience in the security and payment industry and is currently a security technology consultant advising many companies. Malloy was responsible for developing the online authentication product line while at NagraID Security (Oberthur) and prior to that he was Business Development and Marketing Manager for Secure Smart Card ICs for both Philips Semiconductors (NXP) and Infineon Technologies. Malloy originally comes from Boston where he was educated and has M.S. level degrees in Organic Chemistry and an M.B.A. in Marketing. Presently he is the Chairman of The Initiative for Open Authentication (OATH) and is a solution provider with DualAuth. OATH is an industry alliance that has changed the authentication market from proprietary systems to an open-source standard-based architecture promoting ubiquitous strong authentication used by most companies today. DualAuth is a global leader in trusted security with two-factor authentication include auto passwords. He resides in southern California and in his spare time he enjoys hiking, kayaking, and traveling around this beautiful world.

Nathaniel Engelsen is a technology executive, agilest, writer, and speaker on topics including DevOps, agile team transformation, and cloud infrastructure & security. Over the past 20 years he has worked for startups, small and mid-size organizations, and $1B+ enterprises in industries as varied as consulting, gaming, healthcare, retail, transportation logistics, and digital marketing. Nathaniel’s current security venture is Callback Security, providing dynamic access control mechanisms that allow companies to turn off well-known or static remote and database access routes. Nathaniel has a bachelor’s in Management Information Systems from Rowan University and an MBA from the University of Minnesota, where he was a Carlson Scholar. He also holds a CISSP.

The podcast can be heard here.

More information on Abstract Forward Consulting can be found here.

Disclaimer: This podcast does not represent the views of former or current employers and/or clients. This podcast will make every reasonable effort to verify facts and inferences therefrom. However, this podcast is intended to entertain and significantly inform its audience based on subjective reason-based opinions. Non-public information will not be disclosed. Information obtained in this podcast may be materially out of date at or after the time of the podcast. This podcast is not legal, accounting, audit, health, technical, or financial advice. © Abstract Forward Consulting, LLC.

Cybersecurity Firm Imperva Discloses Data Breach

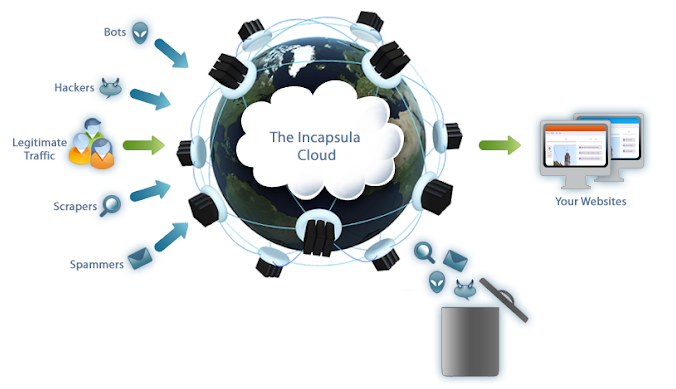
Imperva, formally Incapsula, disclosed on 08/27/19 a data breach impacting its many customers. The company focuses on cyber-security and DDoS mitigation and consulting, heavily via its cloud web application firewall (WAF).

Fig. 1. Imperva, 2019.incapcloud

The breach was discovered 08/20/19 via a third-party. Unfortunately, the exposure goes back to 09/15/17 which means they were compromised at least in part for more than two full years! Clearly, this is evidence of poor internal controls. The exposed data includes customer email addresses, hashed and salted passwords; and API keys and customer-provided SSL certificates — for a partial portion of the exposed data.

Don’t count on cyber security and software firms to be more secure than any other type of company. This breach is likely to negatively impact sales, product design, and will trigger a few investigations, and at least one lawsuit. Additionally, the insurance claim question is a loaded one — and is dependent on how much due diligence the company did before the breach.

To learn more about how to stop data breaches like these at your organization consider attending the Cyber Security Summit this fall.

  • The Ninth Annual Cyber Security Summit, “Pushing the Cyber Security Envelope,” takes place Oct. 28-30, 2019, at the Minneapolis Convention Center in Minneapolis, Minn.
  • The Summit has given awards to top leaders in industry, government and academia since 2015. However, for 2019 the awards program was expanded to include a wider array of visionaries.
  • New this year, women in Cyber, PLUS 16 Tech Sessions, along with Healthcare & Med Device Cyber Security.  Check out this Star Tribune piece from Summit co-chair Catharine Trebnick and colleague Kyle Bauser on this very important topic.
  • To stay up to date on the Summit and top cyber security issues, follow the Cyber Security Summit on social media: Twitter, Facebook, LinkedIn, YouTube. Follow the hashtag #cybersummitMN for the latest conversations on this top matter.

As Summit co-founder Eileen Manning stresses in a well-circulated cover story for Upsize Magazine, cyber security is fundamental for small businesses that work with larger companies, which require it – not to mention for pure survival.

Data breaches like the one at Imperva are likely to increase so interested parties should come together to learn, debate, and flesh out solutions for a more secure future!

U.S. Healthcare Orgs and the GDPR: A New Wave of Privacy Is Blowing In From Europe

4131.jpgIn the United States (US), healthcare organizations and providers have much experience with the Health Insurance Portability Accountability Act (HIPAA), and other pertinent federal laws and regulations. Now, with the new European privacy regulations, the General Data Protection Regulation (GDPR), Europe’s new framework for data protection laws, should cause many U.S. healthcare organizations to think well beyond information security and patient privacy.
Keith-Daniels.jpgNow, important considerations will also include data flows, handling data, cross-border data transfer, data privacy, security monitoring and overall policy compliance for international patients. For those healthcare organizations that offer services in the European Union (EU) or service European Union citizens, then the GDPR, which took effect on May 25, 2018, is a new burden.
The GDPR is designed to standardize data privacy and protection laws across Europe, but it will impact processes, technology, relationships and communication internationally. The new obligations pertain to any organization that handles EU data, whether that organization is in the EU or not. U.S. healthcare organizations will need to safeguard EU patients’ data based on the GDPR in addition to HIPAA and other U.S. regulations. The GDPR fundamentally changes how personal and sensitive data can be used, processed, managed, stored, deleted and disclosed and applies whether an organization is a data controller or data processor.

Healthcare organizations with operations in the EU or who collect personal data in Europe on EU citizens (even such things as collecting business cards at a conference in the EU) will clearly be within the GDPR regime.

The GDPR rules now in force could see a great increase in the penalties slapped on firms for past data breaches, with fines levied at a maximum of 4% of global revenues – which seems excessive, but is intended to be scary.  One major change from most US laws on data breach reporting is that the regulations requires organizations notify authorities of a data breach within 72 hours and, if the breached data is of a serious personal nature, that those individuals whose data has been breached also be notified within 72 hours.

Now, those healthcare organizations subject to GDPR will need to prove that they have adequate processes in place to manage and protect EU residents’ “personal data.” The regulator who manages GDPR in each country may request written documentation in support of GDPR compliance.  Key requirements of the GDPR include:

1)     Appoint a Data Protection Officer (DPO) responsible for data processing.

2)     Document privacy and security policies and procedures.

3)     Implement GDPR special codes of conduct.

4)     Measure effectiveness of privacy and security compliance controls.

5)     Implement risk-based approach for data processing.

6)     Define risks presented by data processing activities.

7)     Implement Data Protection Impact Assessment (Article 35).

8)     Define implement controls and processes related to potential security threats, vulnerabilities and breaches.

9)     Utilize pseudonymization and encryption as controls – a data management and de-identification procedure by which personally identifiable information fields within a data record are replaced by one or more artificial identifiers.

10)  Regulate controls to ensure the ongoing confidentiality, integrity, availability (CIA), and resilience of systems and services

11)  Enable restoration of availability and access to data and services, in a timely manner, in the event of a security incident.

12)  Implement process for regularly testing, assessing, and evaluating the effectiveness of technical and organizational measures.

13)  Right to erasure (‘right to be forgotten’).

In conclusion, an organization’s CEO and Board of Directors are responsible for GDPR compliance as well as complying with American laws. They must ensure that practices are balanced with all cybersecurity and data privacy regulations that apply to their organization. If not done properly, organizations will leave themselves vulnerable to huge fines and criminal consequences under the GDPR, damage to their public reputations, the possibility of additional penalties in the U.S. and securities lawsuits. Multinationals and their US business partners can expect to have to answer underwriters’ queries as to their compliance with GDPR when they are buying or renewing their cyber liability and management liability policies for the next several years.

As the number and breadth of massive data breaches increase, pressure will build on politicians to enact new statutes and regulations with a focus on making corporate management and boards responsible parties for protecting personal information. GDPR is going to be an important “test case” that other countries and jurisdictions will watch closely. New regulations and statutes such as GDPR are mandating that boards and individual directors become focused and engaged on cybersecurity issues. Now, individual directors may be personally responsible for cybersecurity-related issues. There is currently a lack of cyber knowledge on boards of directors in general.

It is unlikely that the threat of holding individual directors responsible for cybersecurity will abate. Data breaches which are reported almost daily have raised the general level of distrust of “big business”, such as the recent criticism of the officers of Experian and Uber and many others before them, and a corresponding increase in the desire to hold top executives personally responsible. In response to these trends, directors must increase their cybersecurity skills, engagement and awareness to comply with the GDPR and the likely next wave of cyber laws and regulations.

Cyber and D&O underwriters will also be closely monitoring these developments and we can expect changes in policy forms to occur as the risks evolve and any negative loss trends become apparent.

For U.S. healthcare organizations subject to GDPR, a demonstrable effort to comply is mandatory, and time is critical.  It seems that the regulators are not requiring immediate and total compliance. Rather, they are looking for entities to be able to show that they are making steps towards compliance and are moving forward with what yet needs to be done. Almost all healthcare organizations, whether now subject to the GDPR or not, will soon also face new laws, such as have just been passed in California (and due to be in effect in 2020), which will bring GDPR-type regulations to the USA itself.

Writer Keith Daniels, JD, CIPP/US[1]
Editor Jeremy Swenson, MBA, MSST

[1] Keith Daniels, JD, CIPP/US is a graduate of the University of Wisconsin – Eau Claire and the University of Wisconsin Law School. He has practiced law in Wisconsin and Illinois and has been involved in cyber liability insurance since its inception around the year 2000. Keith is a Sr independent cyber privacy, compliance, data protection, and risk liability consultant who partners with Abstract Forward Consulting. He is located in Minneapolis, MN and can be reached on LinkedIn here.

British Airways Data Breach Likely The First GDPR Rollback Test.

On 08/21/18 British Airways (BA) suffered the start of a data breach which ended on or about 09/05/18. A UPS (uninterruptible power supply) failure and subsequent power surge was partly how the breach was exacerbated. It was also indicated that a third party (vendor) was involved in some way which complicates liability and brings supply chain security more into scope.

The breach allowed cyber criminals to steal personal and financial information from about 380,000 customers who booked directly with the airline in the preceding two weeks (Ivana Kottasová, CNN, 09/07/18). When a passenger makes a booking through the BA website, they must submit their name, e-mail address, address, and credit or debit card details including: the number, expiration date, date, and the security code or “Card Verification Value” (CVV) — all of this was compromised.

Yet most interestingly, this is one of the first major data breaches since GDPR came into effect in May this year, Walters said (Samuel Gibbs, the Guardian, 09/07/18). “It appears that the company notified the Information Commissioner’s Office and customers within the GDPR’s mandatory 72 hours but the breach will now be investigated and the company could be penalized if it did not take all the necessary measures to protect customer data” (Samuel Gibbs, the Guardian, 09/07/18).

The GDPR rules now in force could see a great increase in the penalties slapped on firms for past data breaches, with fines levied at a maximum of 4% of global revenues. For British Airways’ this amounts to about $630 million dollars based on last years revenue (Gwyn Topham, the Guardian, 09/06/18).

Yet many observers see fines this hefty as counterproductive and the catalyst to push business outside of the EU. Moreover, many international law firms and economists have doubts about the applicability of the GDRP outside of the EU, citing state sovereignty, and free enterprise protection in the United States, etc. The courts will likely further define the context of GRPRs applicability and may roll its reach back some. It is way to early to know what GDPR means in practicality but pushback is coming from well funded, well organized, well researched powerful law and business interest groups. GDPR is dangerously overbroad and ambiguous as echoed in this law firm newsletter (Wendy Butler Curtis and Jeffrey McKenn, Orrick, Herrington & Sutcliffe LLP, 09/09/18). We welcome the debate for a better more modern GDPR.

6 Pronged Approach to Data Exfiltration Detection

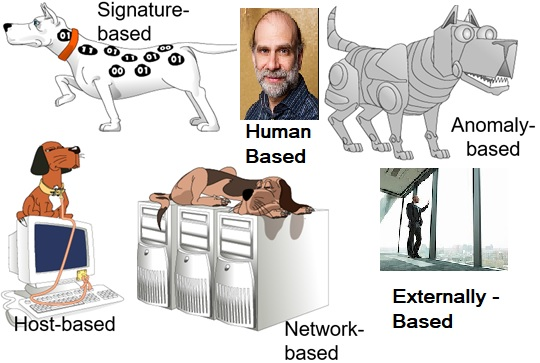
The best way to detect precursors to data exfiltration is to employ a six-prong detection approach applied to all risk areas as practicable. Figure 1. shows the six-pronged detection approach.

Figure 1. Six-Pronged Data Exfiltration Precursor Detection Approach [1] [2].

1) Signature Based.

Characteristics: 1) Uses known pattern matching to signify attack; 2) Former zero days, known exploits, etc.

Advantages: 1) Widely available; 2) Most antivirus is based heavily on this; 3) Fairly fast; 4) Easy to implement; 5) Easy to update.

Disadvantages: 1) Cannot detect attacks for which it has no signature – Zero days; 2) Insider threat.

2) Host Based.

Characteristics: 1) Runs on a single host; 2) Can analyze audit-trails, logs, the integrity of files and directories, etc.

Advantages: 1) More accurate than NIDS; 2) Less volume of traffic so less overhead.

Disadvantages: 1) Deployment is expensive; 2) No plan for if the host gets compromised – Real risk for organizations with more than 10 thousand employees.

3) Human Based [2].

Characteristics: 1) Has the unique experience set deriving intuition; 2) Has five senses.

Advantages: 1) Has the ability to learn multiple tools and connect the dots; 2) Can set team direction and inspire people; 3) Can think creatively; 4) Can think with the voice of the customer or recipient of a phishing e-mail.

Disadvantages: 1) Bias and ego; 2) Cannot calculate large numbers fast.

4) Anomaly Based.

Characteristics: 1) Uses statistical model or machine learning engine to characterize normal usage behaviors; 2) Requires big data and other software tools; 3) Recognizes departures from normal as potential intrusions.

Advantages: 1) Can detect attempts to exploit new and unforeseen vulnerabilities; 2) Can recognize authorized usage that falls outside the normal pattern.

Disadvantages: 1) Generally slower, more resource intensive compared to signature-based tools; 2) Greater complexity, difficult to configure; 3) Higher percentages of false alerts.

5) Network Based.

Characteristics: 1) NIDS (network intrusion detection system) examine raw packets in the network passively and triggers alerts.

Advantages 1) Easy deployment; 2) Unobtrusive; 3) Difficult to evade if done at the low level of network operation.

Disadvantages: 1) Fail Open; 2) Different hosts process packets differently; 3) NIDS needs to create traffic seen at the end host; 4) Need to have the complete network topology and complete host behavior; 5) Highly unlikely.

6) Externally Based.

Characteristics: 1) Studies show there are 258 externally measurable characteristics about network infrastructure (without any inside info).

Advantages: 1) Beaching marking – identifying mismanagement symptoms such as poorly configured DNS or BGN networks; 2) Beaching marking – identifying malicious activity which mostly includes SPAM, phishing, and port scanning; 3) One study found it to be highly reliable in predicting breaches (90% true positives in a closed limited test) [3].

Disadvantages: 1) Its low hanging fruit – easy weaknesses to spot; 2) Good I.T. audits and red teaming is similar.

[1] Dash, Debabrata. “Introduction to Network Security”. PowerPoint presentation. 2017.
[2] Photo of public figure Bruce Schneier by Per Ervland. https://www.schneier.com/ 2018.
[3] Liu, Yang; Sarabi, Armin; Zhang, Jing; Naghizadeh, Parinaz; Karir, Manish; Bailey, Michael; and Liu, Mingyan. “Cloudy with a Chance of Breach: Forecasting Cyber Security Incidents” 2015. Pg. 1.

Decryption Options For 3 Ransomware Types

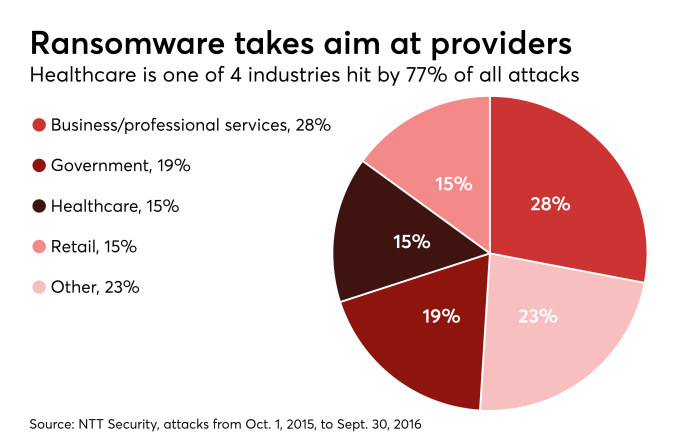
ransomware-main.pngRansomware is on the rise and is going after more victims with little to no defenses, small to medium-small sized businesses and even quiet non-profits. Here are a few tools with a valid track record of stopping and removing 3 common types of ransomware.
1) LockCrypt is a ransomware discovered in June 2017 but is still active in various mutations. It spreads by brute forcing Remote Desktop Protocol credentials – a key port (3389) that should be obviously locked. A prominent example of this exploit occurred in December 2017 when an employee opened an email which was maliciously sent from another co-worker’s account. This was merely an attempt to trick the person to click on the malicious attachment which was appended to the letter. Once it was opened, the ransomware download began after which 48 out of 500 servers of North Carolina County were compromised with LockCrypt (Ugnius Kiguolis, Spyware.com, 12/11/17).

As per Bitdefender, this ransomware family has several sub-variants with the following specific extensions, the first (.1btc) is decryptable with this free Bitdefender tool and the others may be decryptable with the free Trend Micro Malwarebytes Ransomware File Decryptor tool (check for updates).

  1. .1btc (decryptable and included in this version of the tool)
  2. .lock (decryptable, not included in our tool)
  3. .2018 (decryptable, not included in our tool)
  4. .bi_d (not decryptable)
  5. .mich (decryptable, not included in our tool)

2) The five-year-old ransomware Trojan-Ransom.Win32.Rakhni has received a facelift recently which now allows it to decide whether or not to install its traditional ransomware or to drop a cryptominer.

The malware is delivered through spam campaigns where the email comes with a PDF attached which the receiver is prompted to save and then enable editing. When the victim attempts to open the document he or she is presented with an executable that portrays itself as an Adobe Reader plugin and it asks the person to allow it to make changes to their computer (Doug Olenick, SC Magazine, 07/06/18).

According the Kaspersky labs, the current injection chain on this newer exploit is largely the same as before. However, the malware moves along a rather complex path before it decides which form it will take. During the process it will check to make sure the device is not a virtual machine, it will check for and disarm an AV software and also Widows Defender and finally erase most of the footprints made during the malware installation.

The executable, which is written in Delphi and has its strings encrypted, then presents a message box that states the PDF could not be opened, basically to keep the victim from thinking anything negative is about to happen (Doug Olenick, SC Magazine, 07/06/18).

It first checks that the device has one of the substrings:

  1. \TEMP
  2. \TMP
  3. \STARTUP
  4. \CONTENT.IE
  5. Registry check

It then checks to see if the registry contains checks that in the registry there is no value HKCU\Software\Adobe\DAVersion and if it finds this is so it creates HKCU\Software\Adobe\DAVersion = True (Doug Olenick, SC Magazine, 07/06/18). As of Feb 2018 Kaspersky Labs has a free decryption tool (since updated) to get rid of most variations of this infection.

3) Thousands of LabCorp’s servers were impacted by the SamSam ransomware attack on 07/13/18, a CSO online report confirmed (Steve Ragan, 07/19/18). Early information indicates that the company contained the spread of the infection and neutralized the attack within 50 minutes – great. However, before the attack was fully contained, 7,000 systems and 1,900 servers were negatively impacted; 350 were production servers (Steve Ragan, CSO Online, 07/19/18. This is a growing trend in the healthcare sector that reached 15% in 2016 (Fig1. Greg Slabodkin, Health Data Management, 04/11/18).

Fig. 1.
Ransomeware Health.pngAs per Jessica Davis of HealthcareITnews, “SamSam is the virus that shut down the Allscripts platform for about a week in January 2017 and is known to use brute force RDP (remote desktop protocol) attacks to breach a system and spread. The variant is also responsible for taking down Hancock Health, Adams Memorial and the government systems of Atlanta — among a host of others” (HealthcareITNews.com, 07/20/18).

The ransom note it displays is quite interesting, giving the option of randomly-selected file encryption (if you don’t pay the full amount). They’ll also unlock one file for free as a token of trust that they will give your files back after payment (Christopher Boyd, Malwarebytes Labs, 05/01/18).

Fig 2.
samsam-ransomware-infected-file-sensorstechforum-com-sorry-for-files-html-virus
The virus has been updated a couple of times. Currently, it appends one of the following file extensions (Julie Splinters, spyware.com, 06/23/18):

  1. .weapologize;
  2. .AreYouLoveMyRansFile;
  3. .breeding123;
  4. .country82000;
  5. .disposed2017;
  6. .fucku;
  7. .happenencedfiles;
  8. .helpmeencedfiles;
  9. .howcanihelpusir;
  10. .iaufkakfhsaraf;
  11. .mention9823;
  12. .myransext2017;
  13. .noproblemwedecfiles;
  14. .notfoundrans;
  15. .prosperous666;
  16. .powerfulldecryp;
  17. .supported2017;
  18. .suppose666;
  19. .VforVendetta
  20. .Whereisyourfiles;
  21. .wowreadfordecryp;
  22. .wowwhereismyfiles;
  23. .loveransisgood.

Different variants of the virus might drop different versions of ransom notes. However, at the moment victims might receive one of these ransom notes in:

  1. 0009-SORRY-FOR-FILES.html,
  2. IF_WANT_FILES_BACK_PLS_READ.html,
  3. 000-PLEASE-READ-WE-HELP.html,
  4. 000-No-PROBLEM-WE-DEC-FILES.html,
  5. READ-FOR-DECCCC-FILESSS.html,
  6. HELP_DECRYPT_YOUR_FILES.HTML,
  7. 001-HELP_FOR_DECRYPT_FILE.html,
  8. 006-READ-FOR-HELLPP.html,
  9. PLEASE_READ_FOR_DECRYPT_FILES_[Number].html,
  10. PLEASE-README -AFFECTED-FILES.html.

SamSam is the newest and most powerful of the three types of ransomeware mentioned above. There is no known decryption tool or fix for data that you don’t already have your data backed up. Yet it is known to uses tools such as Mimikatz to steal valid user credentials and common IT management tools to move malware to new hosts. Attackers and their malware are increasingly reliant on Mimikatz and similar tools, such as PsExec — associated with everything from PoS malware to webshells — to spread through the network and do damage (Dark Reading, 06/20/18, Ajit Sancheti). Stay tuned here for updates regarding a stable decryption tool for SamSam.