Inside the $6.3 Billion Binance Hack: What Happened, Who Was Hit, and What It Means

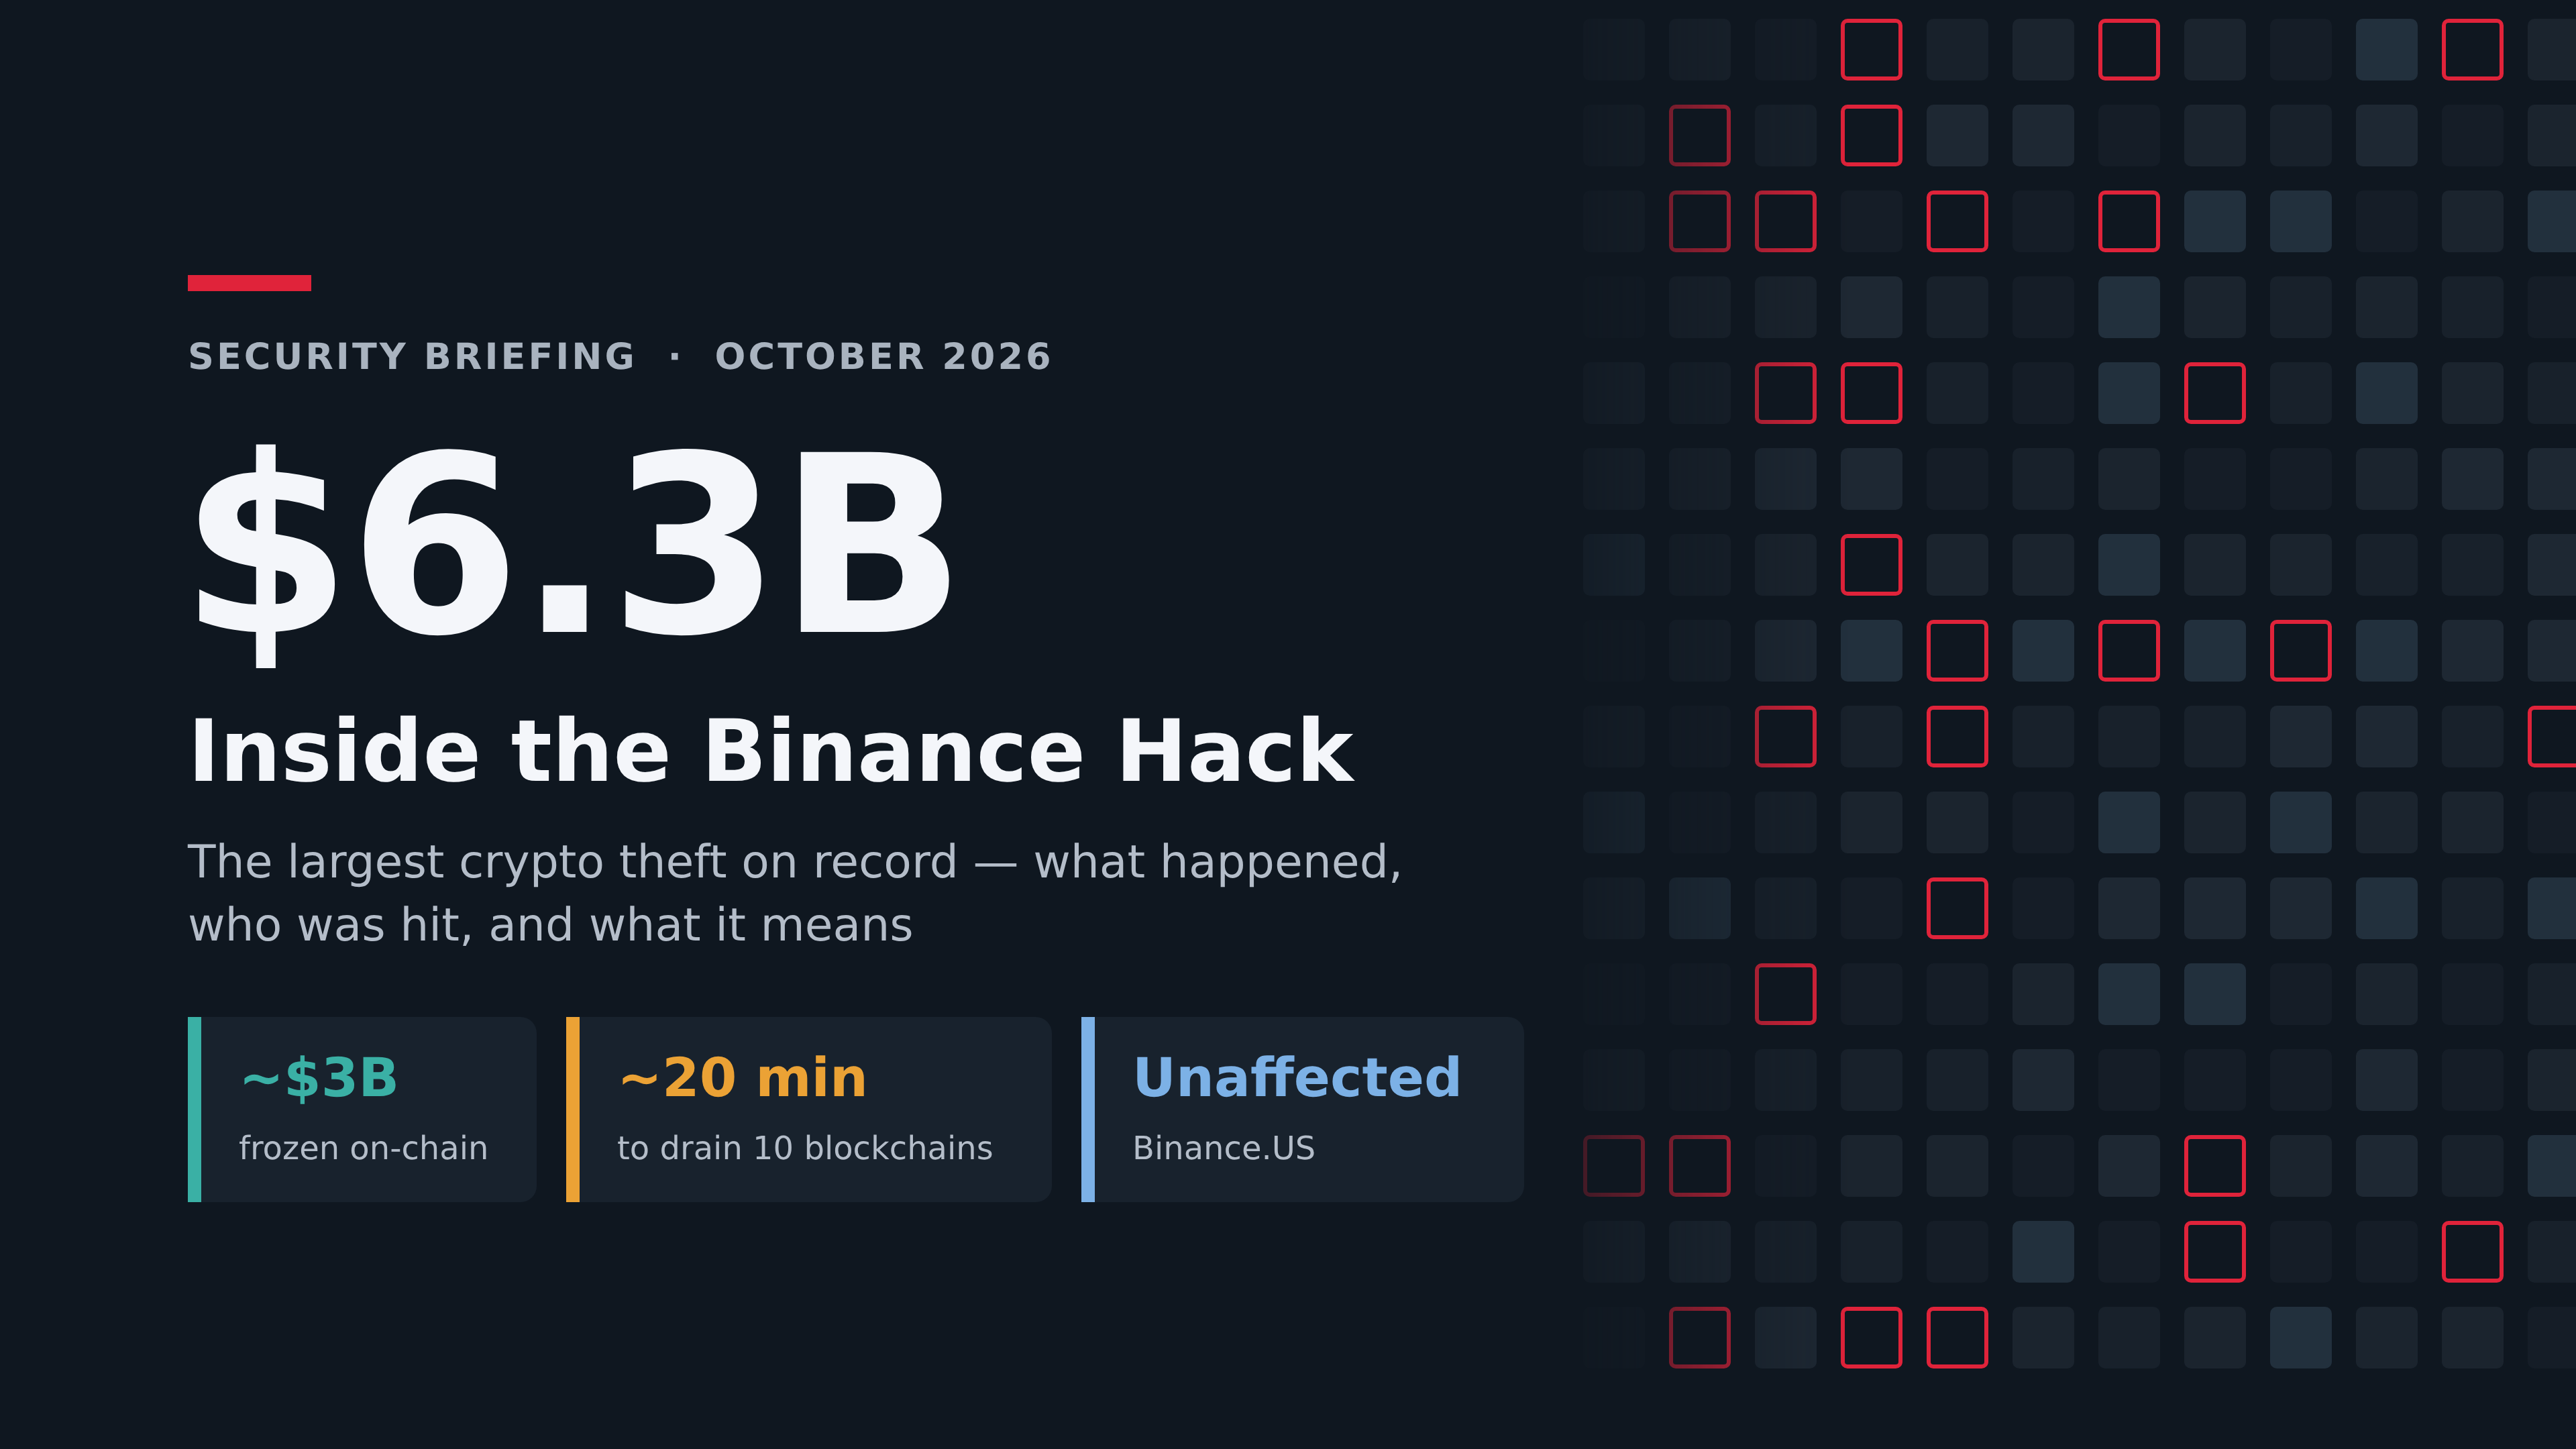
Infographic illustrating the $6.3 billion Binance hack in October 2026.

Figure 1. The $6.3 Billion Binance Hack Title Infographic. Jeremy Swenson. October 2026.

On Thursday night, the world’s largest cryptocurrency exchange suffered what is now the largest theft in the industry’s history. Roughly $6.3 billion in digital assets left Binance’s hot wallets in a matter of minutes, more than four times the $1.5 billion taken from the exchange Bybit in February 2025, the previous record.[1] What follows is what we know so far, what it means for customers, including users of Binance.US, and the lessons that security, risk, and finance leaders should take from it.

What Happened

On the evening of October 29, on-chain researchers began flagging unusually large outflows from Binance wallets. Within the hour, Binance co-founder Changpeng Zhao acknowledged publicly that the activity looked like a hack, and the exchange paused withdrawals across multiple networks.[2] The blockchain analytics firm TRM Labs estimates that approximately $6.36 billion was moved out of Binance wallets across ten blockchains, most of it within about twenty minutes.[3] Binance’s own estimate puts the total impact at about $6.3 billion, and the company has cautioned that the figure may rise as tracing continues.[4]
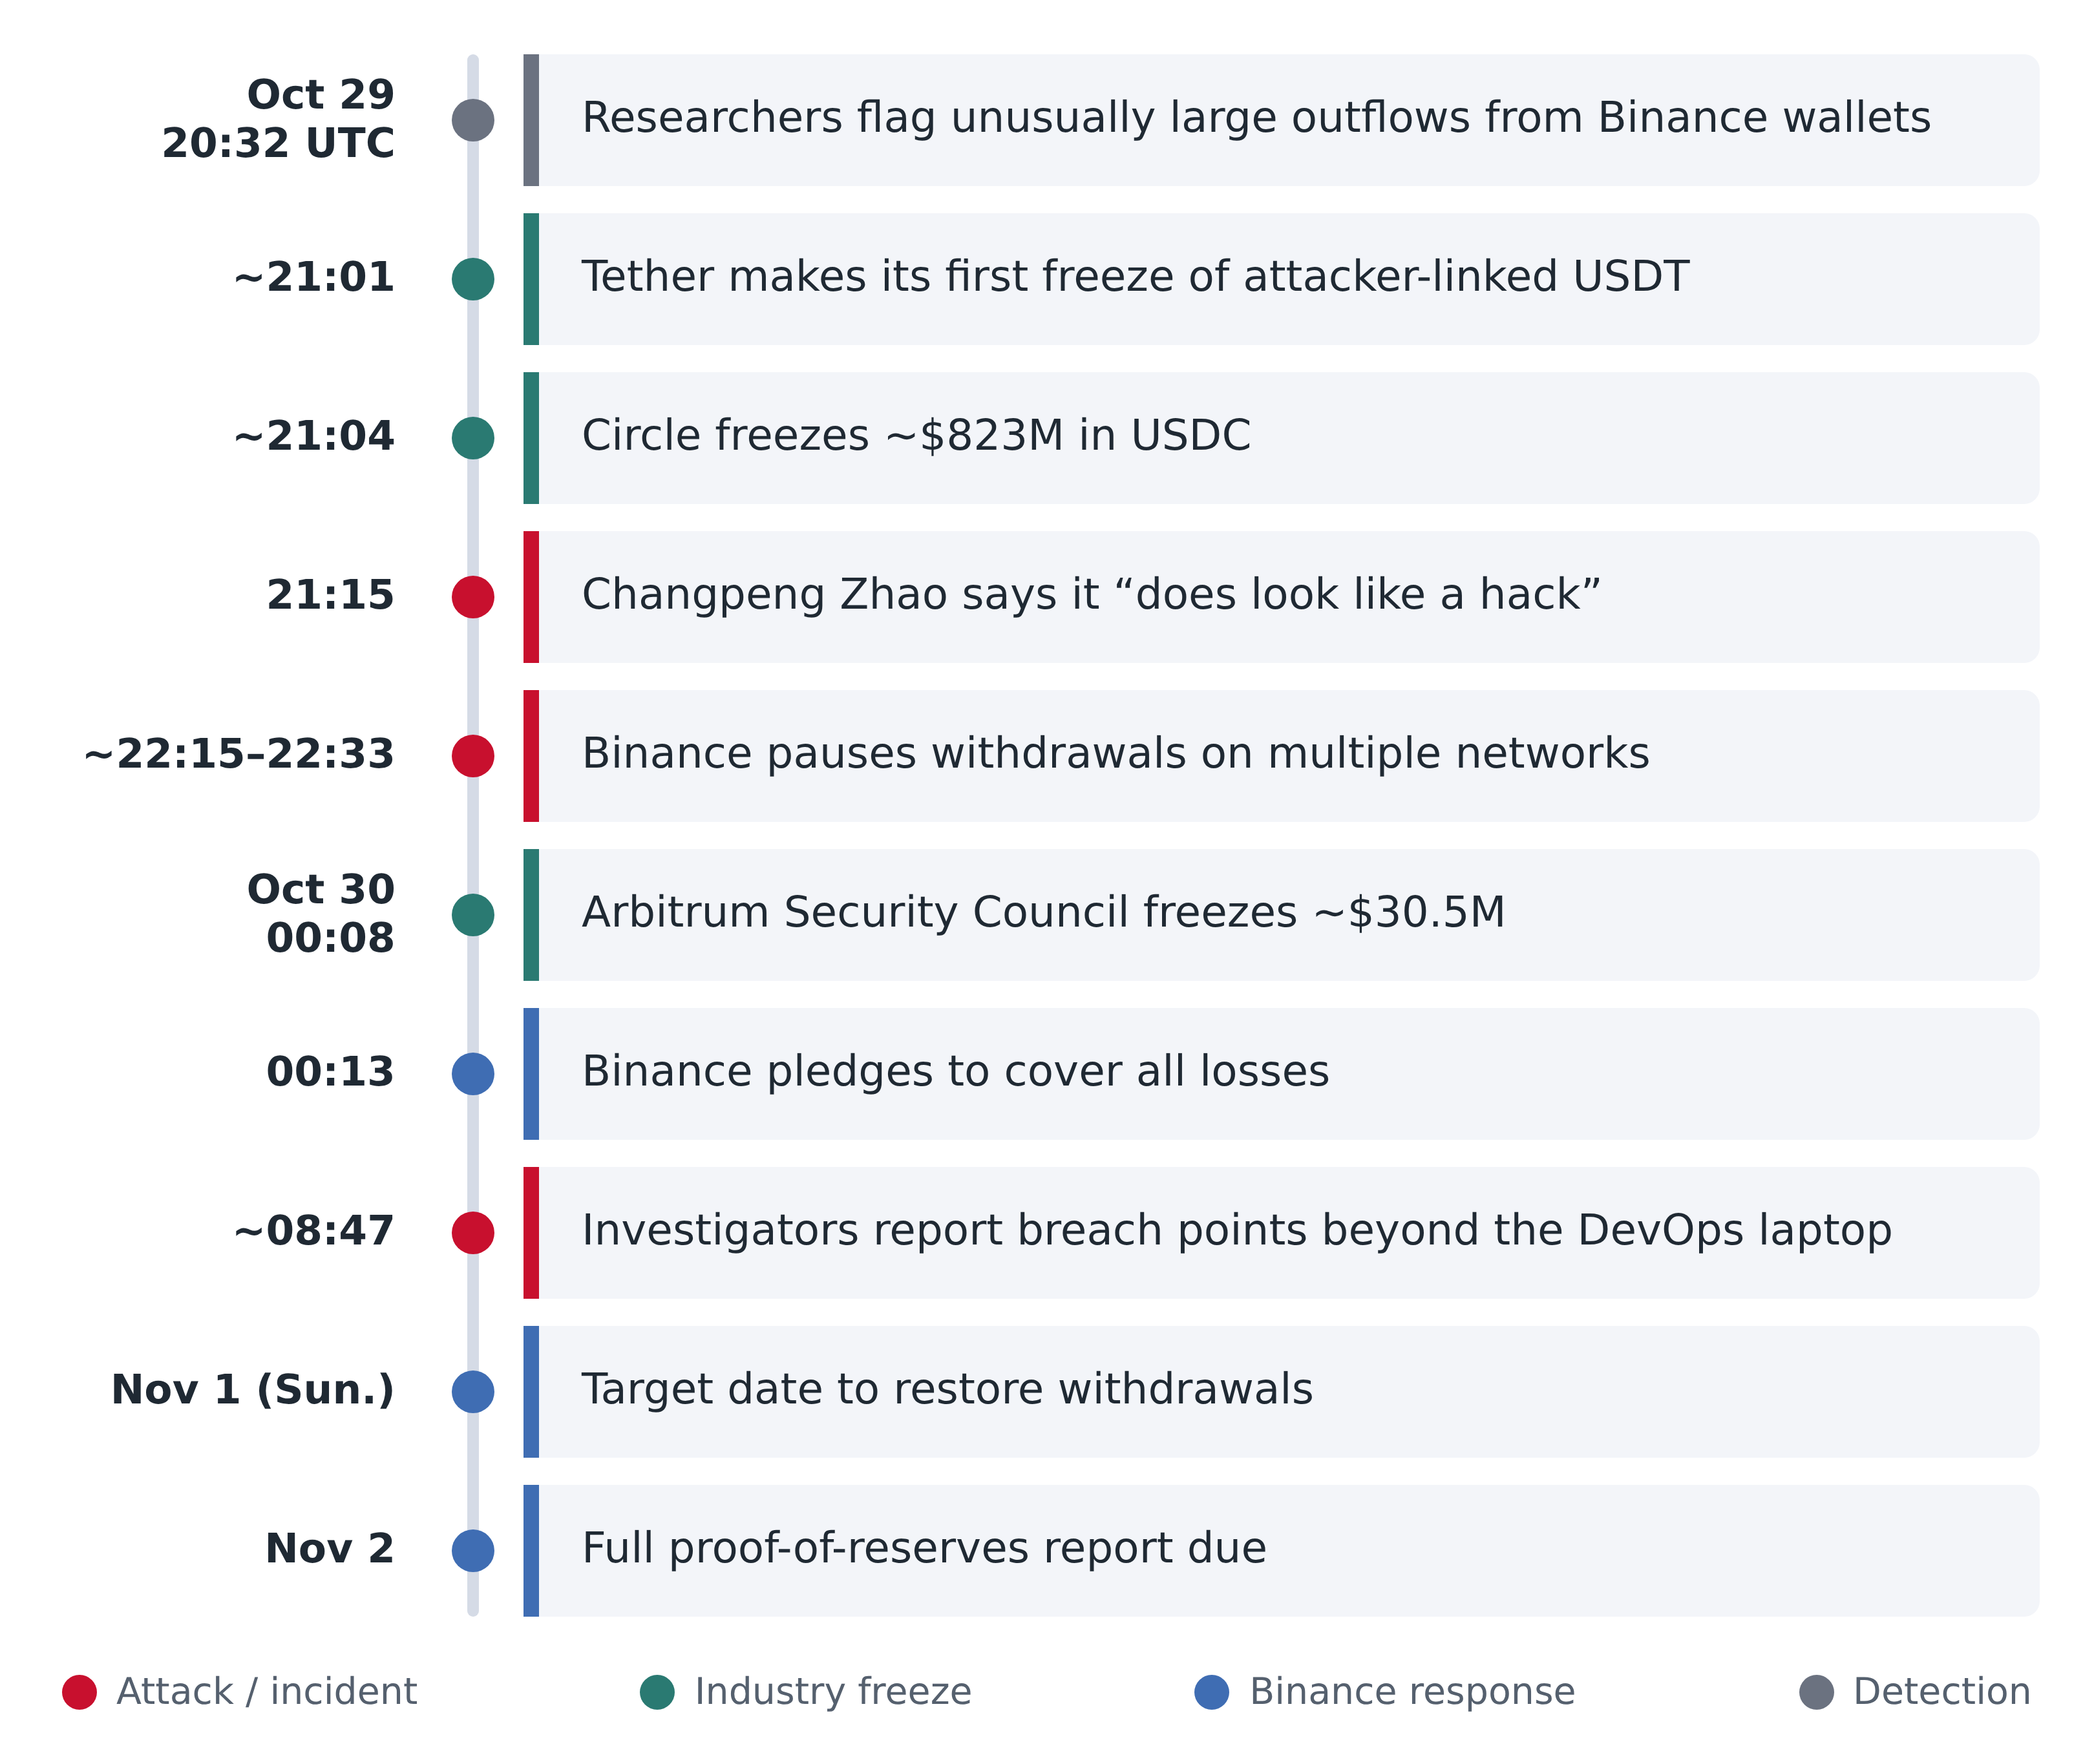
Timeline infographic depicting the Binance hack from October 29 through November 2, 2026. Events are presented in approximate Coordinated Universal Time (UTC), noting that reported times vary across sources.

Figure 2. Timeline of the Binance hack, October 29–November 2, 2026. Times are approximate and in Coordinated Universal Time (UTC); reported times differ across sources. Jeremy Swenson. Data from Crypto Times, HackenProof, Bloomingbit, and statements by Binance, Tether, Circle, and the Arbitrum Security Council.[5] October 2026.

How the Attackers Got In

Binance’s first explanation pointed to a single entry point: a compromised laptop belonging to a DevOps engineer, which reportedly allowed the attacker to reach a service container and submit unauthorized withdrawal transactions.[6] That picture has since grown more complicated. Co-CEO Richard Teng has said the breach was not a one-click event but a more complex, multistage attack, and Binance’s investigators have identified additional points of breach beyond the laptop.[7] Teng also stated that the team had found no evidence that any wallet private keys were leaked.[8] Teng has also said the attackers used a self-destruct mechanism that erased their tooling and traces as they went, which has made reconstructing the intrusion more difficult.[9]

Not every analysis aligns neatly with that account. The security firm Blockaid’s incident report indicates that eleven Binance hot-wallet keys signed the outgoing transfers, which raises the question of whether the attacker abused Binance’s signing infrastructure rather than stealing keys outright.[10] Binance has promised a full technical post-mortem once its investigation is complete, and that report should reconcile the competing accounts.[11]

Speed and Automation

The pace of the attack stands out as much as its size. In a research report released Friday, Chainalysis found that the attackers not only moved the funds quickly but also laundered the proceeds and destroyed evidence of their operation at an unprecedented speed, a pattern its researchers read as automation running through the entire heist.[12] Eric Jardine, head of research at Chainalysis, told Axios that the transactions came at a frequency and scale that ruled out any person approving them: “It had to have been done by a computer.”[13] Researchers at TRM Labs also found that the attackers began preparing for the operation only about 36 hours before it was launched.[14]

Who Is Behind It

Neither Binance nor the FBI has formally attributed the attack.[15] Two prominent analytics firms, however, point in the same direction. TRM Labs links the theft to a North Korean state-sponsored group, citing hallmarks of earlier operations attributed to that country, including transaction signatures obtained in advance.[16] Several blockchain investigation firms have tied the theft specifically to TraderTraitor, a unit linked to the North Korean government’s Lazarus Group collective and the same group that set the previous record with the $1.5 billion Bybit theft.[17] Elliptic likewise assesses North Korea as the likely culprit and reports that some of the stolen funds reached an address connected to the laundering of a suspected North Korean exploit of the exchange Bitget, though Elliptic notes that this establishes a shared laundering network rather than proving a single attacker.[18] According to a person familiar with the matter cited by Reuters, Binance is working with the FBI and the U.S. Secret Service.[19]

A Decade of North Korean Financial Theft

If the attribution holds, the Binance theft extends a record of state-directed financial crime that stretches back more than a decade. In 2016, North Korean hackers tried to steal nearly $1 billion from Bangladesh’s central bank and got away with $81 million; in 2017, the country was blamed for the WannaCry ransomware outbreak, which disrupted hundreds of thousands of computers in more than 150 countries.[20] Pyongyang has since shifted its focus toward crypto exchanges, partly because digital assets are easier to move and launder across borders, even though such attacks tend to leave a more visible trail on-chain.[21] According to Chainalysis’s Jardine, North Korean operators now take the bulk of the value stolen in any given year, effectively crowding out other threat actors.[22]

The AI Accelerant

Experts warn that the speed on display at Binance may offer a glimpse of how artificial intelligence could further amplify North Korea’s operations. Vijay Balasubramaniyan, chief executive and co-founder of Pindrop Security, said social engineering and automation have become hallmarks of the country’s recent cyberattacks. He added that advances in AI-generated video and audio have enabled North Korean operatives to greatly expand schemes that trick U.S. companies into hiring them for IT jobs.[23] Across Pindrop’s customer base, North Korean applicants accounted for roughly one in every 343 job applications last year; this year the figure is about one in 47. Balasubramaniyan attributes the jump less to any single tool than to the sheer number, low cost, and growing ecosystem of AI tools now available to attackers.[24]

The Industry’s Freeze Response

One of the most striking features of this episode is how quickly the rest of the industry moved. Because a large share of the stolen funds were stablecoins, their issuers were able to freeze them on-chain:[25]

  • Tether froze more than $1.56 billion in USDT linked to the incident.[26]
  • Circle froze more than $800 million in USDC, in coordination with law enforcement.[27]
  • Ripple froze roughly $200 million, and World Liberty Financial, working with the custodian BitGo, froze stablecoins and its own tokens.[28]
  • Arbitrum’s Security Council froze about $30.5 million on its network, and the lending protocol Aave froze its Avalanche markets.[29]

Elliptic reports that stablecoins accounted for about $3.46 billion of the stolen funds and that the attacker was slow to convert them, which gave issuers a window in which to act. The firm has independently verified about $2.84 billion of frozen funds on-chain, close to Binance’s estimate of roughly $3 billion.[30] Binance has not said what has become of the remaining $3.3 billion.[31] Jardine said investigators may still recover some of the unfrozen half if those funds pass through exchange infrastructure whose operators can move quickly enough to freeze them, though he cautioned that it is still early days.[32]
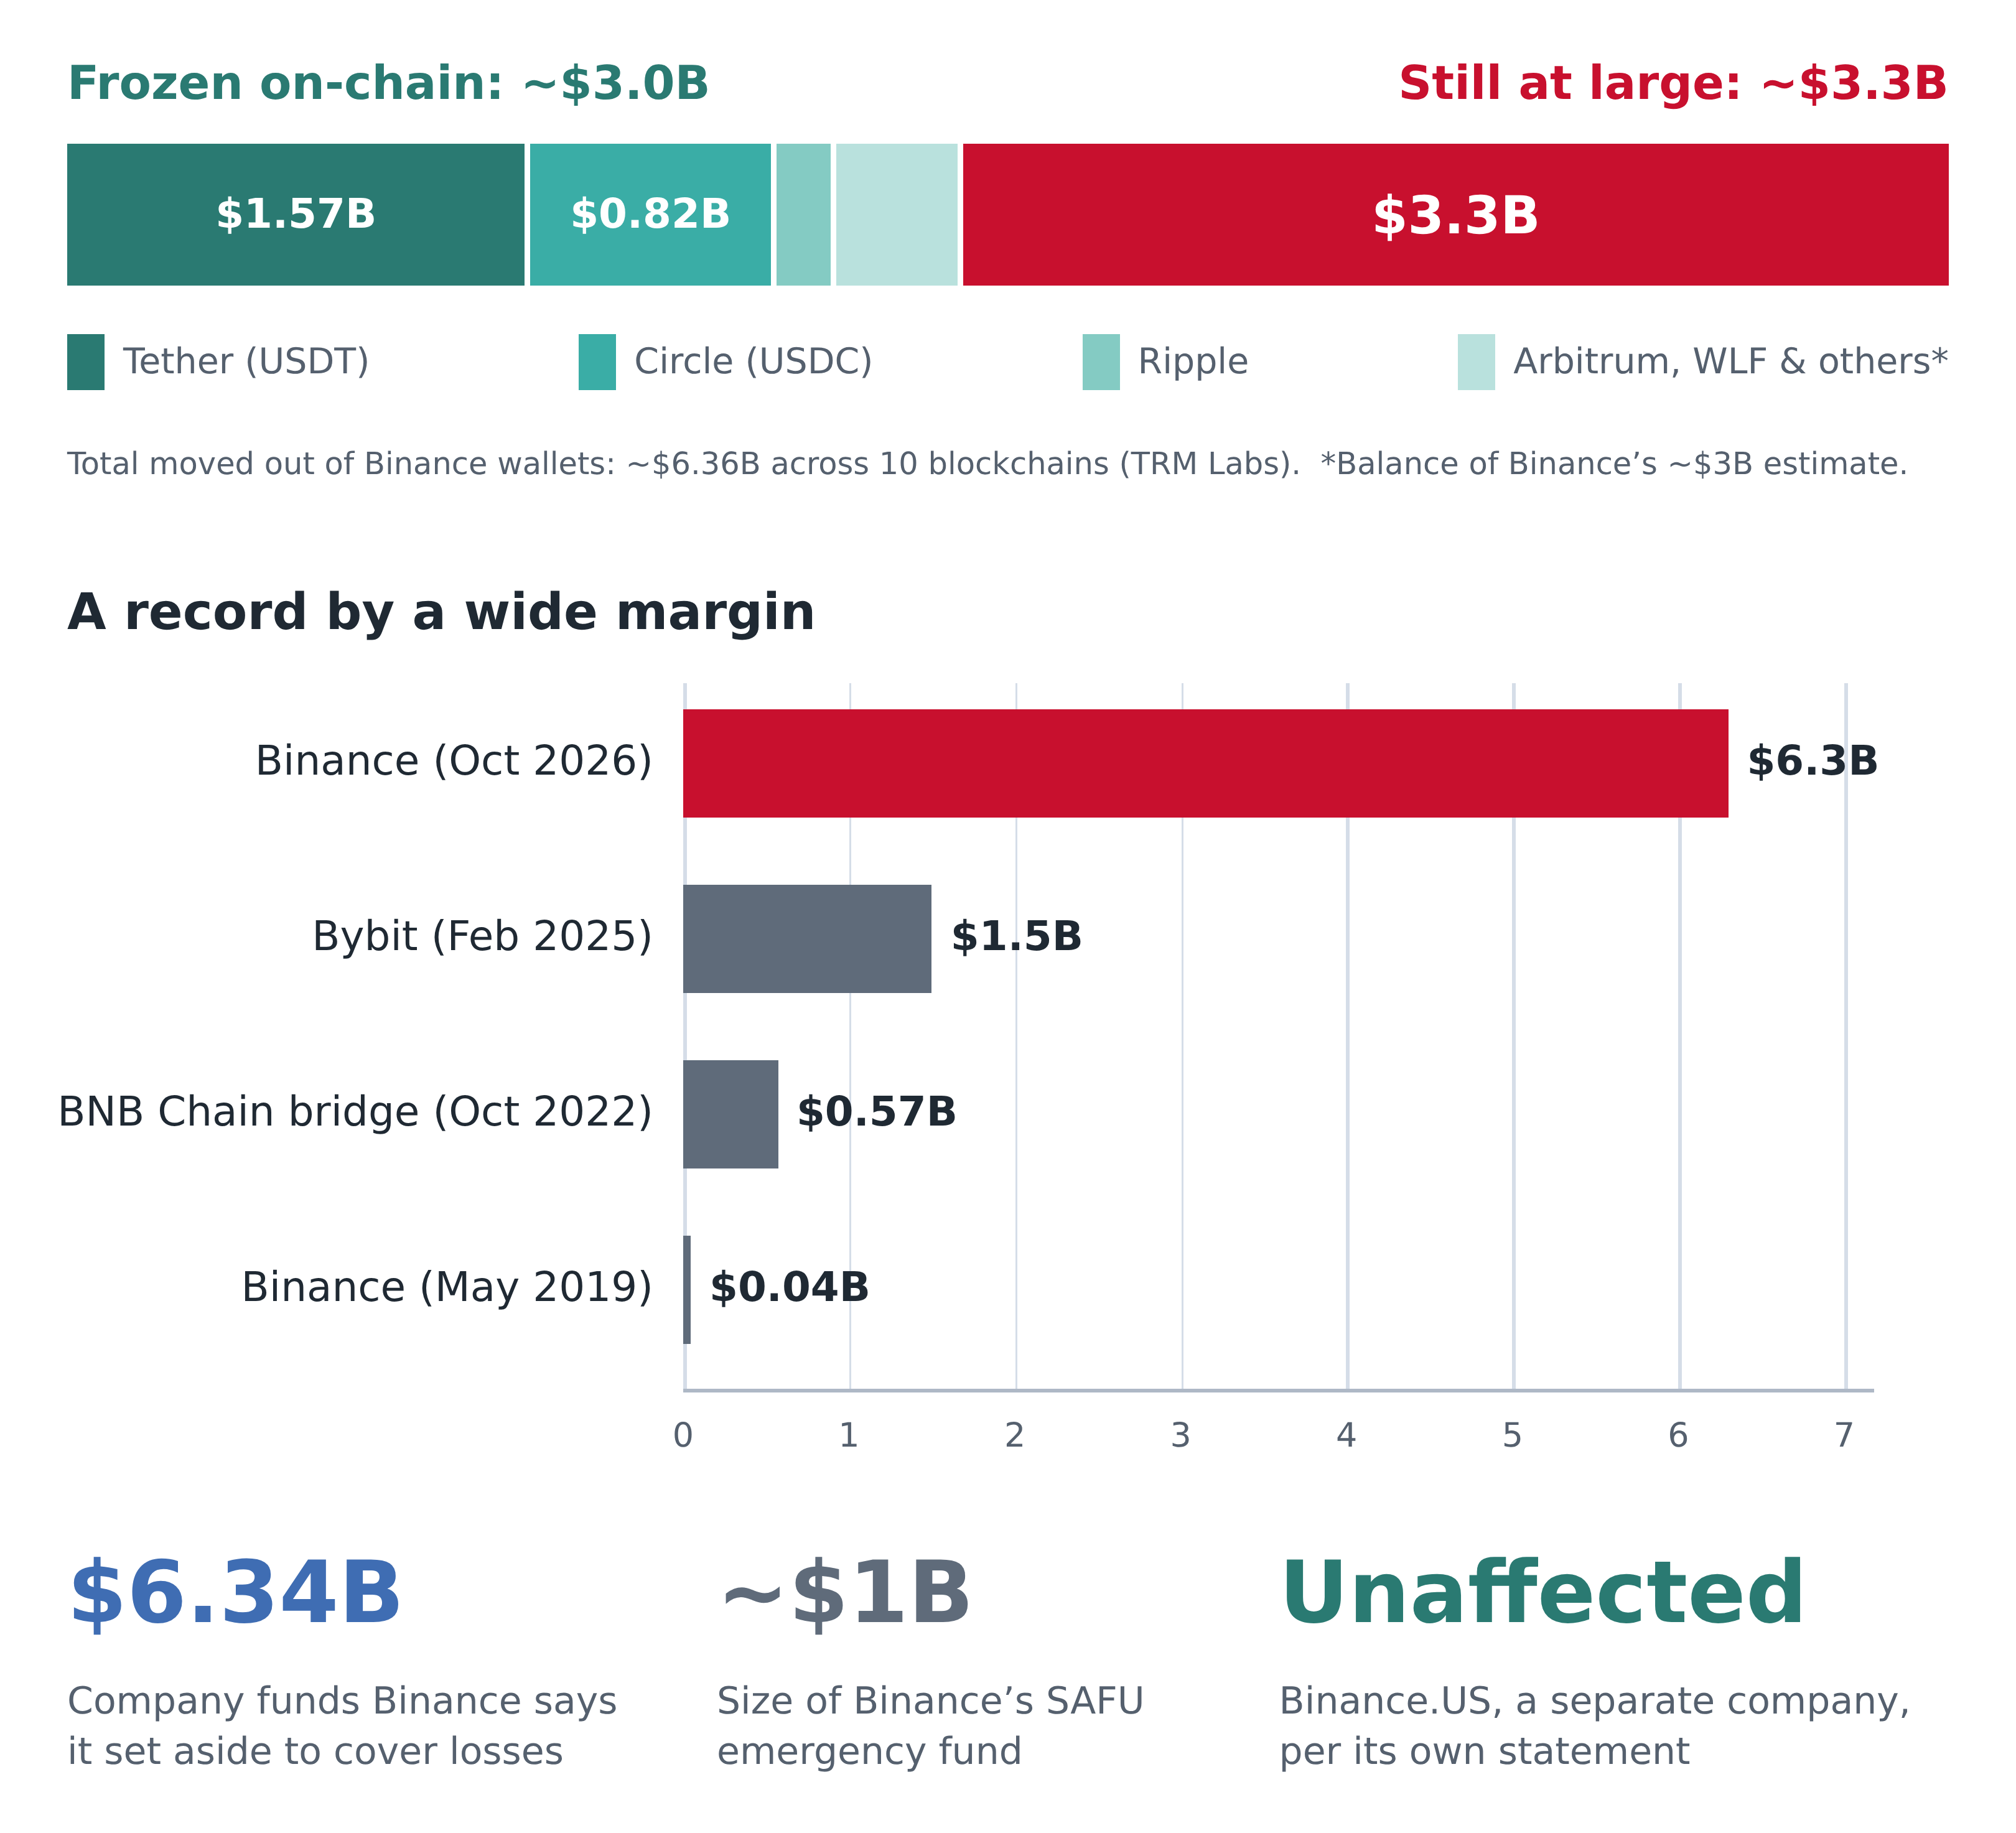
Infographic comparing the status and recovery of assets stolen in the Binance hack with losses from earlier major cryptocurrency exchange hacks, measured in billions of U.S. dollars. Shows reported asset freezes by issuers and Binance, noting that individual amounts may not total Binance’s estimated $3 billion in affected assets.

Figure 3. Status of the stolen assets and comparison with earlier major exchange hacks, in billions of U.S. dollars. Freeze amounts are as reported by issuers and Binance and do not sum precisely to Binance’s ~$3 billion estimate. Jeremy Swenson. Data from Binance, Tether, Circle, Reuters, Elliptic, TRM Labs (via CNBC), Al Jazeera, and Ynet News.[33] October 2026.

Were Customer Funds Stolen?

Binance maintains that customers will not lose money. Teng has said the incident was confined to the exchange’s own hot wallets and that customer assets are managed under a separate security system; Binance says it has secured more than $6.34 billion of company funds to cover the losses in full.[34] That sum is more than six times the size of Binance’s roughly $1 billion Secure Asset Fund for Users (SAFU), the emergency reserve created in 2018 for exactly this kind of event.[35] The company has not detailed where the additional funds came from, but it plans to publish a full proof-of-reserves report by November 2.[36]

In the near term, customers are feeling the effects through access rather than balances. Withdrawals remain suspended while Binance rebuilds its withdrawal system, and the company expects to restore them by Sunday, November 1.[37] Early messaging was also inconsistent: Binance insisted that user funds were completely safe while simultaneously pledging to cover all losses, a combination that understandably confused users.[38] Analysts at Fundstrat Global Advisors say the breach does not currently appear to pose a meaningful solvency risk to an exchange that reported about $162.8 billion in assets under custody and 335 million registered users as of its 2025 annual report.[39]

What About Binance.US?

Binance.US, which operates as a separate company, has said it was not affected, and Coinbase likewise reported no impact on its operations.[40] The one caveat concerns Americans who access the global Binance exchange in spite of its geographic restrictions, for example through a virtual private network; they are in the same withdrawal queue as every other global user.[41]

Market Impact

The hack struck an already fragile market. Bitcoin fell toward $77,000, ether dropped by nearly 6 percent, and Binance’s native BNB token slid by nearly 10 percent.[42] The market maker GSR reported that bid–ask spreads on spot bitcoin at Binance were about five times wider than normal early Friday, a sign of thin liquidity as traders pulled back.[43]

Six Takeaways for Leaders

1. The most privileged endpoints are the biggest attack surface. A single engineer’s laptop appears to have provided an early foothold into systems controlling billions of dollars. Developer and DevOps endpoints deserve the same scrutiny as production infrastructure.

2. Key security is not the same as signing security. Even if no private keys leaked, an attacker who can push transactions through a legitimate signing pipeline can do enormous damage. Authorization logic, withdrawal limits, and anomaly detection along the signing path matter as much as key custody.

3. Centralized controls cut both ways. The ability of Tether, Circle, and others to freeze roughly $3 billion is the main reason this was not a total loss. It is also a reminder that stablecoins carry issuer-level control: a feature in a crisis and a policy debate the rest of the time.

4. Counterparty risk is real, even at the top. If the world’s largest exchange can be breached, institutions and individuals alike should know where their assets sit, who holds the keys, and what happens contractually when something goes wrong.

5. Expect regulation to follow. Industry voices, including the head of Franklin Templeton’s crypto business, are already calling for stronger cybersecurity rules.[44] A theft of this scale gives policymakers fresh momentum on custody standards, proof-of-reserves requirements, and mandatory incident disclosure.

6. Defenses must operate at machine speed. An attack that drained billions in about twenty minutes and erased its own traces leaves no room for manual review. Automated withdrawal circuit breakers, real-time anomaly response, and preserved forensic logs are now baseline controls. With AI-enabled North Korean applicants flooding hiring pipelines, identity verification during recruiting also belongs inside the security perimeter.

The Bottom Line

Binance appears to have the balance sheet to absorb this loss, and a coordinated industry response froze nearly half of the stolen funds within hours. Yet the largest crypto theft in history occurred at the platform best resourced to prevent it. The forthcoming post-mortem will be one of the most important security documents the industry has produced, and it deserves close reading.

How is your organization thinking about custody and counterparty risk after this week? I would welcome your perspective in the comments.

About The Author

Jeremy A. Swenson is a disruptive-thinking security entrepreneur, futurist/researcher, and seasoned senior management technology risk and digital strategy consultant. His experience spans healthcare, retail, financial services, high technology, and government. He is a frequent speaker and published writer, and he also does some pro bono consulting in these areas. He holds a certificate in Media Technology Policy from Oxford University’s Media Policy Summer Institute, an MSST (Master of Science in Security Technologies) degree from the University of Minnesota’s Technological Leadership Institute (TLI), an MBA from Saint Mary’s University of Minnesota, and a BA in political science from the University of Wisconsin Eau Claire. He is an alum of the Federal Reserve Secure Payment Task Force, the Crystal, Robbinsdale, and New Hope Community Police Academy (MN), as well as the Minneapolis FBI Citizens Academy. You can follow him on LinkedIn and Twitter. You can contact him for speaking, media, or consulting engagements via his website here: https://jeremy-swenson.com/

Endnotes


[1]Ravie Lakshmanan, “Binance Suffers Security Breach Affecting $6.3 Billion in Assets, Nearly $3 Billion Frozen,” The Hacker News, October 30, 2026, accessed October 30, 2026, https://thehackernews.com/2026/10/binance-suffers-security-breach.html; “Binance Hit by Record $6.3 Billion Crypto Hack: ‘This Was a Complex Attack,’ Says Co-CEO,” Yahoo Finance, October 30, 2026, accessed October 30, 2026, https://finance.yahoo.com/markets/article/bitcoin-drops-to-76000-as-binance-hack-spooks-investors-tether-circle-freeze-assets-083406383.html.

[2]“Binance Hack: How CZ, Coinbase, Tether and 70+ Crypto Leaders Reacted to the $6.3B Theft,” Crypto Times, October 30, 2026, accessed October 30, 2026, https://www.cryptotimes.io/2026/10/30/binance-hack-how-cz-coinbase-tether-and-70-crypto-leaders-reacted-to-the-6-3b-theft/; “Binance Pauses Withdrawals as Hackers Suspected of Stealing Billions in Crypto,” TechCrunch, October 29, 2026, accessed October 30, 2026, https://techcrunch.com/2026/10/29/binance-pauses-withdrawals-as-hackers-suspected-of-stealing-billions-in-crypto/.

[3]“Binance’s $6.3 Billion Hack: What We Know and What Comes Next,” CNBC, October 30, 2026, accessed October 30, 2026, https://www.cnbc.com/2026/10/30/billions-in-crypto-frozen-in-binance-hack-heres-what-happens-next-.html.

[4]“Binance Targeted in $6.3 Billion Crypto Heist, the Largest Ever,” NBC News, October 29, 2026, updated October 29, 2026, accessed October 30, 2026, https://www.nbcnews.com/business/markets/binance-hack-tether-circle-stablecoins-rcna606445.

[5]Timeline compiled from “Binance Hack: How CZ, Coinbase, Tether and 70+ Crypto Leaders Reacted”; “Binance Hack Update: $6.3B Impact, $3B Frozen After DevOps Laptop Breach,” Crypto Times, October 30, 2026, accessed October 30, 2026, https://www.cryptotimes.io/2026/10/30/binance-hack-6-3b-impact-3b-frozen-after-devops-laptop-breach/; “Binance Hack: What We Know About the $6.3B Breach,” HackenProof (blog), October 30, 2026, accessed October 30, 2026, https://hackenproof.com/blog/binance-hack, which also reports the Arbitrum Security Council freeze; and “Binance CEO Says Full Proof-of-Reserves Report Due Nov. 2, Pledges Full Compensation for Hack Losses,” Bloomingbit, October 30, 2026, accessed October 30, 2026, https://en.bloomingbit.io/feed/news/123309. Binance statements as reported in Lakshmanan, “Binance Suffers Security Breach”; Tether’s as reported in “Binance Targeted in $6.3 Billion Crypto Heist”; and Circle’s as reported in “Binance Hit by $6.3 Billion Theft in What Could Be the Biggest Crypto Heist on Record,” Help Net Security, October 30, 2026, accessed October 30, 2026, https://www.helpnetsecurity.com/2026/10/30/binance-crypto-hack/.

[6]Lakshmanan, “Binance Suffers Security Breach.”

[7]Agence France-Presse, “Crypto Platform Binance Confirms ‘Complex’ $6.3 bn Hack,” Yahoo Finance, October 30, 2026, accessed October 30, 2026, https://finance.yahoo.com/markets/crypto/articles/crypto-platform-binance-confirms-major-013059975.html; “What We Know About the $6.3B Breach.”

[8]“Binance Hack: Teng Says No Private Key Leaked, and Blockaid Says Eleven Binance Keys Signed the Transfers,” FinanceFeeds, October 30, 2026, accessed October 30, 2026, https://financefeeds.com/binance-hack-eleven-keys-signed-no-leak/.

[9]Sam Sabin, “How North Korea Perfected the Crypto Heist,” Axios, October 31, 2026, accessed October 31, 2026, https://www.axios.com/2026/10/31/north-korea-hackers-binance-crypto.

[10]“Teng Says No Private Key Leaked.”

[11]“Binance Hit by $6.3 Billion Theft.”

[12]Sabin, “How North Korea Perfected the Crypto Heist.”

[13]Sabin, “How North Korea Perfected the Crypto Heist.”

[14]Sabin, “How North Korea Perfected the Crypto Heist.”

[15]“Binance Hack: What the $6.3 Billion Theft Means for US Crypto Users,” BreezyScroll, October 30, 2026, accessed October 30, 2026, https://www.breezyscroll.com/money/binance-hack-crypto-assets-frozen.

[16]“What We Know and What Comes Next.”

[17]Sabin, “How North Korea Perfected the Crypto Heist.”

[18]Elliptic, “The Largest Theft in History: North Korea Likely Behind the $6.4 Billion Binance Hack,” Elliptic Insights, October 30, 2026, accessed October 30, 2026, https://www.elliptic.co/insights/binance-largest-hack-in-history/.

[19]Reuters, “Hackers Steal $6.3 Billion from Binance in Record Heist Blamed on North Korea,” Yahoo Finance, October 30, 2026, accessed October 30, 2026, https://finance.yahoo.com/markets/crypto/articles/tether-circle-freeze-2-38-222607515.html.

[20]Sabin, “How North Korea Perfected the Crypto Heist.”

[21]Sabin, “How North Korea Perfected the Crypto Heist.”

[22]Sabin, “How North Korea Perfected the Crypto Heist.”

[23]Sabin, “How North Korea Perfected the Crypto Heist.”

[24]Sabin, “How North Korea Perfected the Crypto Heist.”

[25]“Binance Hit by $6.3 Billion Theft.”

[26]“Binance Targeted in $6.3 Billion Crypto Heist.”

[27]“Binance Hit by $6.3 Billion Theft.”

[28]Reuters, “Hackers Steal $6.3 Billion from Binance.”

[29]“What We Know About the $6.3B Breach.”

[30]Elliptic, “Largest Theft in History.”

[31]“Binance Says $6.3bn Stolen in Biggest Crypto Heist in History: What We Know,” Al Jazeera, October 30, 2026, accessed October 30, 2026, https://www.aljazeera.com/news/2026/10/30/binance-says-6-3bn-stolen-in-biggest-crypto-heist-in-history-what-we-know.

[32]Sabin, “How North Korea Perfected the Crypto Heist.”

[33]Total stolen and Binance’s frozen-funds estimate from Lakshmanan, “Binance Suffers Security Breach”; Tether freeze from “Binance Targeted in $6.3 Billion Crypto Heist”; Circle freeze from “Binance Hit by $6.3 Billion Theft”; Ripple freeze from Reuters, “Hackers Steal $6.3 Billion from Binance”; stablecoin and verified-frozen totals from Elliptic, “Largest Theft in History”; TRM Labs estimate from “What We Know and What Comes Next”; unaccounted-for remainder and earlier-hack comparison from “Binance Says $6.3bn Stolen”; and “Binance Reports $6.3 Billion Crypto Breach, Potentially the Biggest Hack in History,” Ynet News, October 30, 2026, accessed October 30, 2026, https://www.ynetnews.com/business/article/bjmb5f11tme.

[34]“Binance CEO Says Full Proof-of-Reserves Report Due Nov. 2.”

[35]“Binance Says $6.3bn Stolen.”

[36]Reuters, “Hackers Steal $6.3 Billion from Binance.” “Binance CEO Says Full Proof-of-Reserves Report Due Nov. 2.”

[37]“Binance CEO Says Full Proof-of-Reserves Report Due Nov. 2.”

[38]Agence France-Presse, “Binance Confirms ‘Complex’ $6.3 bn Hack.”

[39]“What We Know and What Comes Next.” Reuters, “Hackers Steal $6.3 Billion from Binance.”

[40]“Binance Reports $6.3 Billion Crypto Breach”; “Binance Hack Update.”

[41]“What the $6.3 Billion Theft Means for US Crypto Users.”

[42]“Live Updates: Bitcoin Falls to $77,000 as Binance Exploit Combines with Tech Woes,” CoinDesk, October 30, 2026, accessed October 30, 2026, https://www.coindesk.com/markets/2026/10/30/live-news-binance-hack-rattles-crypto-as-intel-plunges-and-ai-spending-fears-hit-tech; Agence France-Presse, “Binance Confirms ‘Complex’ $6.3 bn Hack.”

[43]Reuters, “Analysts React as Binance Freezes Assets after $6.3 Billion Security Breach,” Euronext Financial News, October 30, 2026, accessed October 30, 2026, https://live.euronext.com/en/financial-news/analysts-react-binance-freezes-assets-after-63-billion-security-breach.

[44]Chris Perkins, “Binance Hack Reveals Need for Stronger Cybersecurity Regulation,” interview, CNBC, video, October 30, 2026, accessed October 30, 2026, https://www.cnbc.com/video/2026/10/30/binance-hack-calls-for-stronger-cybersecurity-regulation-perkins.html.
The Idea Is Sound, the Messenger Still Has to Earn It: A Point-by-Point Response to Mark Zuckerberg’s Superintelligence Manifesto

By Jeremy Swenson

Mark Zuckerberg and the story of Facebook, now Meta, deserve real respect. He beat long odds and reshaped technology, news media, digital marketing, and the organization of commerce on the web. Zuckerberg saw the future of social media before it was imaginable to most people—and no, MySpace does not substantially count.

On August 10, 2026, Zuckerberg published “The Future Is for Everyone,” a philosophy for how superintelligence should be built and governed.[1] Superintelligence, or artificial superintelligence (ASI), is a theoretical form of artificial intelligence that would surpass existing AI—including NLP, generative AI, and agentic AI—with cognitive and potentially emotional capabilities far beyond those demonstrated by humans. We do not know how far away ASI may be, whether it will ever materialize, or whether it will emerge in the form we currently envision. What follows below is my point-by-point response to his fifteen core assertions—where I agree, where I disagree, and how his argument holds up against outside scrutiny—followed by a criticality ranking and my overall conclusion.

Point-by-Point Response:

1. Core philosophy: Zuckerberg frames superintelligence around three pillars: individual empowerment as the source of prosperity, invention as AI’s purpose, and balance of power—not technical alignment—as the foundation of safety. I largely agree, though prosperity means different things to different people and organizations, so “balance of power” would land better reframed as “checks and balances.”

2. Against centralization: He rejects the idea that concentrating superintelligence in a few institutions produces safety, arguing history shows concentrated power rarely stays benevolent. I fully agree—over-centralization tends to increase both abuse and inequality, not reduce them.

3. Historical precedent: He points to electricity, personal computers, and the internet as technologies that sparked fear but ultimately broadened prosperity, crediting individuals over institutions. I only partly agree; most of those individuals still relied on institutional support—national labs, universities, private capital. If “institutions” here means government specifically, I agree more, since government typically receives transformative technology from individuals and their companies, not the other way around.

4. Invention over automation: The essay argues AI’s greatest value is unlimited discovery, not automating existing work. I agree, and would add that automation is largely already here, while true AI invention—new medical, technical, and virtual breakthroughs—is still mostly ahead of us.

5. Distribution as the answer: Meta’s answer to “who controls superintelligence” is to distribute it as widely as possible. I partly agree, but artificial superintelligence does not exist yet, and “distribution” here is really another way of describing the “democratization of technology”—the same dynamic DeepSeek demonstrated by building comparable AI capability with less compute at lower cost.

6. Meta’s product vision: Concrete commitments include personal AI agents with strong privacy, creative and business tools, personalized tutoring, and free or affordable access via a compute auction. I agree with the roadmap in principle, but the company’s own track record on privacy and bias raises a fair question: why should we expect this time to be different? In 2018, Cambridge Analytica improperly harvested data from 87 million Facebook users, and the fallout led to a then-record $5 billion FTC settlement the following year, back when the company still operated as Facebook rather than Meta.[2]

7. Balance-of-power reasoning: Using thought experiments—a superintelligent lawyer, a cybersecurity tool—he argues risk flips from dangerous to beneficial once capability is broadly distributed. I think this overgeneralizes; outcomes depend on the specific use case and the quality of the inputs, not distribution alone. TechCrunch’s Zoë Schäffer made a similar point more bluntly, calling the superintelligent-lawyer example “a loaded example.”[3]

8. Jobs and the economy: He predicts individual capability growth can outpace automation, producing new jobs and more, smaller, entrepreneurial companies rather than mass unemployment. I agree in principle—as people offload basic tasks to AI, their capacity for deeper work should grow in turn. But Bill Gates’s companion essay on the AI transition is far less confident on timing, warning AI could be either “the greatest equalizer ever invented, or the worst source of injustice,”[4] and naming job losses—especially entry-level roles—as an urgent, near-term risk rather than a problem the market will smoothly absorb.

9. Infrastructure and communities: Meta’s “Community Compact” promises local jobs, trade training, low energy prices, and water-positive data centers. I remain neutral to skeptical here, and I’m not alone. Rest of World surveyed AI researchers across Africa, Asia, and Latin America who concluded that “Meta has grossly overstated the economic benefits of its data centers,”[5] noting that construction jobs are temporary while permanent operational staffing stays minimal.

10. Security risks (cyber/bio): Zuckerberg argues defenders need a resource advantage and proposes labs share intermediate model checkpoints with government. I agree; attackers only need to succeed once, while defenders must be right every time—an asymmetry that only grows as infrastructure becomes more complex.

11. Freedom and government power: Personal agents should have private, even Meta-inaccessible modes, while government still gets early technical access through lab collaboration. I think this oversimplifies a genuinely hard problem, but it correctly signals that U.S. citizens’ rights need clearer application in the digital and AI era, particularly around privacy and protection from undue persecution.

12. American leadership: The U.S. must accelerate infrastructure, maintain export controls on rivals, and reduce policy friction so American open-source models can lead. I agree the U.S. leads in infrastructure buildout today, but we cannot afford to underestimate China’s high-tech trajectory.

13. Redefining alignment: Rather than aligning AI to a company’s centralized values, Meta frames alignment as serving each user’s own goals. This needs more research and public discussion before we know what it means in practice, but the underlying principle—that a company shouldn’t override individual values—is sound.

14. Controlling recursive self-improvement: To avoid a single dominant superintelligence, most compute should stay directed toward individual goals, with competing labs providing natural checks and balances. I agree, and note this closely echoes the “People and Planet” component of NIST’s AI Risk Management Framework stakeholder lifecycle.[6]

15. Governance commitments: Meta will route model-release safety decisions through independent board oversight rather than one person’s judgment, and will continue supporting open-source releases. I agree governance like this is necessary for a company like Meta, though it’s worth noting Meta’s own Oversight Board has drawn criticism as underpowered and politicized.

Points Ranked by Criticality:

Table 1. My own ranking, from highest to lowest stakes for society and safety—not Zuckerberg’s own ordering, which follows the structure of his essay rather than relative importance.

RankPointWhy It Ranks Here
1Controlling recursive self-improvementExistential-level stakes; if mishandled, undermines every other safeguard in the essay.
2Governance commitmentsThe actual mechanism for holding Meta accountable to everything else it promises.
3Security risks (cyber/bio)Near-term, high-severity risk with a structural attacker/defender asymmetry.
4Freedom and government powerCore civil-liberties question with no easy technical fix.
5Balance-of-power reasoningThe central logical claim the rest of the essay depends on.
6Against centralizationFoundational premise underneath most of the other points.
7American leadershipMajor geopolitical and economic stakes over the medium term.
8Core philosophySets the interpretive frame for the entire essay.
9Redefining alignmentDetermines whether personal AI agents can be trusted at scale.
10Distribution as the answerPractical mechanism, but contingent on superintelligence actually arriving.
11Jobs and the economyHigh real-world impact and the most immediate to most readers’ lives.
12Meta’s product visionConcrete and near-term, but company-specific and trust-dependent.
13Invention over automationImportant framing, but lower near-term risk or controversy.
14Historical precedentMostly rhetorical; interpretation matters more than the underlying facts.
15Infrastructure and communitiesReal impact, but localized rather than systemic.

Overall Conclusion:

Taken as a whole, I think Zuckerberg is right about the diagnosis more than the cure. His central claim—that no single “benevolent” superintelligence can exist because human values genuinely conflict, and that safety is therefore a balance-of-power problem rather than a purely technical one—is the strongest and most defensible idea in the essay. I agree with it fully, and I think it deserves more attention from policymakers than it has received.

The essay is weaker in treating “distribute it to everyone” as a sufficient answer on its own, rather than as the starting point for a harder set of questions about who actually gets meaningful access, on what terms, and under whose governance. TechCrunch’s critique lands here: Zuckerberg keeps “reminding us of all the ways it’s likely to go wrong”[7] even as he argues the future will be fine, and that tension is never fully resolved. The Rest of the World’s reporting adds a second gap: “everyone” in the essay quietly assumes reliable power, connectivity, and functioning regulatory protections—conditions that do not hold for much of the world Meta says it wants to empower.

Gates’s companion essay is the most useful outside check on Zuckerberg’s optimism, precisely because Gates does not disagree that AI could be transformative—he simply thinks the transition will be rockier, more unequal, and more urgent than Zuckerberg’s framing allows for, and that it requires coordinated international action rather than one company’s product roadmap and governance promises.

My overall verdict: Zuckerberg presents a genuinely useful philosophical framework—favoring a balance of power over centralized control—but neither his essay nor Meta’s track record demonstrates that the company’s governance is strong enough to serve as a trusted steward of superintelligence. That concern is particularly difficult to ignore given the timing: as Zuckerberg calls for broader trust in Meta’s vision for superintelligence, the company has agreed to pay up to roughly $17 billion to settle allegations involving harm to young users, privacy, and the design of its social platforms.[8] Meta denies wrongdoing, but the contrast is telling. It is hard not to view the essay, at least in part, as a strategically timed PR effort accompanying the settlement announcement. The idea may be sound, but the messenger still has to prove it—and earn that trust over time, across different communities and through demonstrated governance, transparency, and accountability.

Endnotes:


[1] Mark Zuckerberg, “The Future Is for Everyone,” Meta, August 10, 2026, https://www.meta.com/thefutureisforeveryone/.

[2] Federal Trade Commission (FTC), “FTC Imposes $5 Billion Penalty and Sweeping New Privacy Restrictions on Facebook,” press release, July 24, 2019, https://www.ftc.gov/news-events/news/press-releases/2019/07/ftc-imposes-5-billion-penalty-sweeping-new-privacy-restrictions-facebook.

[3] Zoë Schäffer, “Mark Zuckerberg’s AI Manifesto Is Exactly Why People Don’t Like AI,” TechCrunch, August 10, 2026, https://techcrunch.com/2026/08/10/mark-zuckerbergs-ai-manifesto-is-exactly-why-people-dont-like-ai/.

[4] Bill Gates, “The Turbulent AI Era Is Here. The Choices We Make Now Are Critical,” LinkedIn, August 26, 2026, https://www.linkedin.com/pulse/turbulent-ai-era-here-choices-we-make-now-critical-bill-gates-kkmze/.

[5] Ananya Bhattacharya, “It’s laughable”: Global AI experts challenge Zuckerberg’s “AI for everyone,” Rest of World, August 20, 2026, https://restofworld.org/2026/mark-zuckerberg-meta-ai-for-everyone-manifesto-global-critique/.

[6] National Institute of Standards and Technology (NIST), AI Risk Management Framework (AI RMF 1.0), NIST AI 100-1 (Gaithersburg, MD: U.S. Department of Commerce, January 2023).

[7] Zoë Schäffer, “Mark Zuckerberg’s AI Manifesto Is Exactly Why People Don’t Like AI,” TechCrunch, August 10, 2026, https://techcrunch.com/2026/08/10/mark-zuckerbergs-ai-manifesto-is-exactly-why-people-dont-like-ai/.

[8] John Ruwitch, “Meta, states agree to $17 billion settlement in child safety trial,” NPR, August 26, 2026, https://www.npr.org/2026/08/26/nx-s1-5944781/meta-settlement-child-safety-lawsuit.

From Mythos to Fable: What Business Leaders Must Learn from the New AI Governance Crisis

Anthropic Claude Mythos InfoSec Infographic, generic rights-free, 2026.

The Mythos Moment Just Got Bigger

A few weeks ago, Anthropic’s Mythos model was being celebrated as a breakthrough in AI-enabled cybersecurity. Reports suggested it could identify software vulnerabilities at unprecedented speed, accelerate remediation efforts, and potentially transform how organizations secure critical infrastructure. Some observers described it as one of the most capable cyber-focused AI systems ever developed.¹

Today, the conversation looks very different. The White House has ordered Anthropic to suspend access to Mythos 5 and Fable 5 for foreign nationals, citing national security concerns. Reports indicate that government officials were concerned not only about potential jailbreak vulnerabilities but also about the possibility that a China-linked group may have accessed the models.² The administration reportedly fears that advanced frontier models could be reverse-engineered through model distillation techniques, allowing strategic competitors to replicate key capabilities.³

Whether those concerns ultimately prove justified is almost beside the point. For business leaders, the real lesson is not about Anthropic. It is about the future of AI itself. The Mythos controversy signals that AI governance is rapidly evolving from a technology management issue into a business resilience, geopolitical risk, and digital supply chain challenge.⁴

The New Reality: AI Is Becoming Strategic Infrastructure

For years, organizations treated cloud computing as utility infrastructure. Access was largely assumed. The same cloud services were available whether you were in Minneapolis, Mumbai, London, or Singapore. Artificial intelligence appeared to be following a similar trajectory.

That assumption may no longer hold. The government’s restrictions on Mythos and Fable represent one of the first major examples of an advanced AI model being treated more like sensitive defense technology than commercial software.⁵ In effect, policymakers are beginning to ask whether some AI systems should be governed similarly to advanced semiconductors, encryption technologies, or military capabilities.

If that trend continues, organizations may find that access to critical AI capabilities can be restricted, delayed, licensed, monitored, or even revoked based on national security considerations.⁶ That should concern every executive currently building long-term business strategies around AI-enabled operations.

Why Business Leaders Should Care

Many executives may be tempted to dismiss the Mythos controversy as a dispute between Anthropic and the federal government. That would be a mistake. The more important story is not whether Anthropic’s safeguards were sufficiently robust or whether a jailbreak vulnerability actually existed. The real story is that organizations are rapidly becoming dependent on AI systems they do not own, cannot fully inspect, and may not always be able to access.

Imagine investing millions of dollars to integrate a frontier AI model into cybersecurity operations, software development, customer service, fraud detection, or enterprise decision-making, only to discover that access has been restricted due to a government directive, geopolitical concerns, export controls, or actions taken by the model provider itself. What appeared to be a stable technology platform can quickly become a strategic dependency.⁷

This is precisely why the Mythos situation deserves attention from boards, executives, and risk leaders. The disruption was not caused by a system outage, ransomware attack, or cloud failure. Instead, it emerged from a combination of national security concerns, policy decisions, and uncertainty surrounding advanced AI capabilities. These are risks that many organizations have not yet incorporated into their enterprise risk management programs.⁸

Historically, leaders worried about disruptions involving suppliers, cloud providers, telecommunications carriers, or critical software vendors. Frontier AI models now belong in that same category. Organizations increasingly depend upon a relatively small number of providers for advanced AI capabilities, creating concentration risks that may become more significant as AI becomes embedded in core business processes.⁹

Endnotes

  1. Anthropic, Project Glasswing Technical Findings, June 2026.
  2. Terrence O’Brien, “China May Have Accessed Mythos,” The Verge, June 14, 2026.
  3. Ibid.
  4. Kristian McCann, “Why the US Restricted Anthropic’s Mythos and Fable and What It Means for AI Access,” June 15, 2026.
  5. Hadas Gold, “Anthropic Suspends All Access to Mythos Model After US Government Bans Foreign Nationals Use,” CNN, June 13, 2026.
  6. McCann, “Why the US Restricted Anthropic’s Mythos and Fable.”
  7. Gold, “Anthropic Suspends All Access to Mythos Model.”
  8. O’Brien, “China May Have Accessed Mythos”; Gold, “Anthropic Suspends All Access to Mythos Model.”
  9. McCann, “Why the US Restricted Anthropic’s Mythos and Fable.”

Russia’s Sanctions-Busting Cryptocurrency Empire: Architecture, Actors, and the Future of Financial Conflict

Fig. 1. Russia’s Sanctions-busting Cryptocurrency Empire Infographic, Jeremy Swenson via ChatGPT, 2026.


I. Origins of a Parallel Financial System
:

The roots of Russia’s sanctions-busting cryptocurrency ecosystem can be traced to the intersection of geopolitical pressure and technological opportunity. While Russia experimented with cryptocurrency policy ambiguity throughout the 2010s, it was the aftermath of the 2022 invasion of Ukraine—and the subsequent exclusion from key parts of the global financial system, including SWIFT—that triggered a structural change. Lacking dollar liquidity and limited by Western banking restrictions, Russian policymakers and aligned financial actors started rapidly developing alternative methods for cross-border settlement (1).

Early efforts were fragmented, consisting of informal networks of exchanges, darknet markets, and capital flight channels. Platforms such as Garantex, founded in 2019, became foundational nodes in this system, allowing users to convert rubles into stablecoins and move funds internationally while avoiding traditional compliance mechanisms (6). Despite sanctions imposed by the U.S. Treasury in 2022, these platforms adapted rapidly, shifting wallets, rebranding, and integrating with crypto mixers to obscure transaction flows (1).

By 2024, Russia had formally embraced cryptocurrency for international trade, legalizing its use in cross-border transactions while maintaining domestic restrictions. This dual posture—restrict internally, exploit externally—laid the groundwork for a state-tolerated, if not state-enabled, shadow financial architecture that would mature rapidly in the years that followed (9).

II. The Rise of A7A5 and the Industrialization of Evasion:

The emergence of the ruble-backed stablecoin A7A5 marked a turning point from opportunistic evasion to industrial-scale financial engineering. Developed through networks linked to sanctioned Russian financial institutions and offshore intermediaries, A7A5 was designed explicitly to bypass Western oversight by enabling direct conversion from rubles into crypto assets and then into globally usable currencies (6).

Unlike decentralized cryptocurrencies such as Bitcoin, A7A5 represents a hybrid model: centralized issuance combined with decentralized transaction pathways. This design allows Russian actors to maintain monetary control while leveraging blockchain’s opacity and global reach. Within its first year, the token processed tens of billions of dollars in transactions, with some estimates approaching $100 billion in cumulative volume—evidence of rapid adoption across trade networks and sanctions-affected industries (4).

Crucially, this system extended beyond simple financial transfers. It became embedded in supply chain logistics, enabling the procurement of dual-use goods—technology with both civilian and military applications—through intermediaries in regions such as Central Asia and the Middle East. Crypto-enabled payments allowed these transactions to bypass traditional banking scrutiny, effectively creating a parallel trade infrastructure insulated from Western enforcement mechanisms (3).

III. Decentralization as Strategy, Not Ideology:

In Western culture, decentralization is often seen as a libertarian ideal—an escape from centralized power. However, in the Russian sanctions-evasion model, decentralization is not about ideology but strategy. It is used selectively to reduce visibility, make enforcement harder, and spread operational risk.

This system operates as a layered network rather than a single platform. Exchanges such as Bitpapa and others flagged by blockchain intelligence firms function alongside mixers, peer-to-peer marketplaces, and offshore entities, creating a fluid ecosystem in which assets can be rapidly converted, transferred, and obfuscated (7).

Moreover, decentralization enhances resilience. When Western authorities sanction one node—such as Garantex—activity shifts to successor platforms or newly created entities, often staffed by the same personnel. This phenomenon mirrors adaptive systems: disruption leads not to collapse but to evolution. The result is a sanctions-resistant architecture that thrives on redundancy and ambiguity.

Academic research supports this point by showing that sanctions enforcement in crypto is structurally reactive, while illicit actors are fast and adaptive. Studies find that once wallets or platforms are sanctioned, actors quickly shift funds to new addresses, exchanges, or networks—often within hours—well before regulators can complete attribution and enforcement cycles (12). Because blockchain systems allow unlimited address creation and operate across jurisdictions, enforcement actions tend to disrupt specific nodes rather than the broader network. As a result, the research consistently demonstrates that sanctions evasion persists not despite enforcement, but because the system’s design enables rapid migration and continuity.

IV. The Ransomware Nexus: Criminal Infrastructure and State Alignment

At the heart of Russia’s crypto ecosystem lies a symbiotic relationship between cybercriminal groups and financial infrastructure. Ransomware organizations such as REvil and Ryuk-linked networks have long relied on cryptocurrency to receive and launder payments, targeting Western corporations, critical infrastructure, and supply chains (2).

The connection between these groups and sanctioned exchanges is well-documented. Platforms like Garantex have been identified as facilitating transactions tied to ransomware proceeds, effectively serving as financial clearinghouses for cybercrime (5). This relationship extends beyond mere tolerance. Investigations such as Operation Destabilise have uncovered networks in which cryptocurrency exchanges, money laundering operations, and state-linked actors intersect. In some cases, these networks have been used not only for financial gain but also to support espionage activities and strategic objectives aligned with Russian interests (11).

The implication is clear: ransomware is not simply criminal activity but a component of a broader hybrid warfare strategy. By targeting Western institutions and funneling proceeds through crypto networks, these groups generate revenue, disrupt adversaries, and reinforce Russia’s alternative financial ecosystem.

V. Extraction from the West: Mechanisms of Digital Theft:

The Russian crypto-sanctions ecosystem extracts value from the West through multiple channels, blending cybercrime, financial engineering, and trade manipulation. Ransomware attacks represent the most visible vector, with payments often demanded in cryptocurrency and subsequently laundered through exchanges and mixers (2).

However, a less visible but equally significant mechanism is trade-based money laundering facilitated by crypto. Russian entities purchase restricted goods through intermediaries, paying in stablecoins that are difficult to trace. These goods are then re-exported into Russia, effectively bypassing export controls (3).

Additionally, capital flight and asset concealment play a major role. Wealthy individuals and sanctioned entities move funds into crypto assets to protect them from seizure, leveraging decentralized wallets and offshore exchanges. The cumulative effect is a steady outflow of value from regulated Western systems into a shadow economy that operates beyond their reach.

By 2025, illicit cryptocurrency flows had surged dramatically, with tens of billions of dollars linked to sanctions evasion and state-aligned networks (10).

VII. Conclusion: The Future of Financial Warfare:

Russia’s sanctions-busting cryptocurrency empire represents a new phase in the evolution of financial conflict—not simply a workaround, but a scalable model for a decentralized, state-influenced financial system operating beyond traditional controls. What began as a reaction to Western sanctions has matured into a resilient ecosystem that blends state policy, criminal enterprise, and technological innovation. Its strength lies in its hybridity: centralized where control is necessary, decentralized where opacity provides advantage.

For the West, this presents a fundamental challenge. Traditional tools—sanctions, asset freezes, and banking restrictions—are increasingly limited in a world where adversaries can operate outside the formal financial system. Countering this shift requires more than incremental reform; it demands a transition from static enforcement to dynamic, intelligence-driven financial defense.

A central component of this approach is the expansion of blockchain analytics and real-time monitoring. On-chain intelligence has proven effective in tracing illicit flows and identifying high-risk actors, but its true value emerges when integrated into coordinated international enforcement frameworks. Moving beyond periodic sanctions designations toward continuously updated, intelligence-led responses will be critical to keeping pace with adaptive networks (7).

Equally important is targeting the infrastructure that enables liquidity. Cryptocurrency ecosystems depend on exchanges, stablecoin issuers, and fiat on-ramps and off-ramps to function. Coordinated regulation and enforcement against these access points—particularly across jurisdictions that facilitate intermediary flows—can significantly constrain the usability of sanctions-evading assets. While measures such as wallet blacklisting and exchange sanctions have had impact, they must evolve from reactive tools into part of a broader, proactive strategy (1).

At the same time, deterrence must be redefined. Financial penalties alone are insufficient against actors who operate in decentralized and jurisdictionally fragmented environments. Effective deterrence will require a combination of cyber operations, asset seizures, and coordinated disruption of ransomware and illicit financial infrastructure. Public-private collaboration will be essential, as much of the expertise and visibility into these networks resides within the private sector.

Beyond enforcement, the West must also compete. Developing secure, efficient, and transparent alternatives—such as regulated digital payment systems, central bank digital currencies, and compliant stablecoin frameworks—can reduce the relative attractiveness of shadow financial networks. If legitimate systems offer greater speed, cost efficiency, and accessibility, the incentive to rely on illicit alternatives diminishes.

Finally, this issue must be understood in its broader geopolitical context. Russia’s crypto ecosystem is not an isolated case but part of a wider movement toward financial fragmentation, in which states seek parallel systems to reduce dependence on Western institutions. Addressing this trend will require sustained international coordination, including strategic engagement with non-Western jurisdictions that play intermediary roles in these networks (4).

In this evolving landscape, success will not be measured by the elimination of illicit systems, but by the ability to constrain, outpace, and adapt to them. The future of financial warfare will belong to those who can align technological capability with strategic coherence—building financial architectures that are not only secure, but resilient against continuous disruption.

Bibliography:

  1. U.S. Department of the Treasury. “Treasury Sanctions Cryptocurrency Exchange and Network.” https://home.treasury.gov/news/press-releases/sb0225
  2. Chainalysis. Crypto Crime Report 2026. https://www.chainalysis.com
  3. Royal United Services Institute (RUSI). “The Shadow Crypto Economy Feeding Russia’s War Machine.” https://www.rusi.org
  4. Center for European Policy Analysis (CEPA). “A Crypto River Runs Through Russia.” https://cepa.org
  5. BankInfoSecurity. “U.S. Sanctions Crypto Exchange Tied to Russian Ransomware.” https://www.bankinfosecurity.com
  6. TRM Labs. “Garantex, Grinex, and the A7A5 Token.” https://www.trmlabs.com
  7. Elliptic. “Russia-Linked Crypto Platforms’ Ongoing Sanctions Evasion.” https://www.elliptic.co
  8. Reuters. “Sanctioned Russian Crypto Exchange Suspends Services.” https://www.reuters.com
  9. Business Insider. “Russia’s Crypto Shadow Economy.” https://www.businessinsider.com
  10. Financial Times. “Illicit Crypto Flows Surge to Record Levels.” https://www.ft.com
  11. National Crime Agency. “Operation Destabilise.” https://www.nationalcrimeagency.gov.uk
  12. Zola, Francesco et al. “Assessing the Impact of Sanctions in the Crypto Ecosystem.” https://arxiv.org/abs/2409.10031

Chinese Hackers Stole About 614GB of Data from Unnamed U.S. Navy Contractor

A series of cyber attacks backed by Chinese government hackers earlier this year infiltrated the computers of a U.S. Navy contractor, allowing a large amount of highly-sensitive data on undersea warfare to reportedly be stolen. Likely by A People’s Liberation Army unit, known as Unit 61398, which is filled with skilled Chinese hackers who pilfered corporate trade secrets to benefit Chinese state-owned industry. The breaches, which took place in January and February 2018, including secret plans to develop a supersonic anti-ship missile for use on US submarines by 2020, according to American officials.

This data was of a highly sensitive nature despite it being housed on the contractor’s unclassified network – putting it here was mistake and exacerbated vulnerabilities. A contractor who works for the Naval Undersea Warfare Center in Newport, R.I. — a research and development center for submarines and underwater weaponry — was the target of the hackers, the Post reported. While the unnamed officials did not identify the contractor, they told the newspaper that a total of 614 gigabytes of material was taken. Included in that data was information about a secret project known as Sea Dragon, in addition to signals and sensor data and the Navy submarine development unit’s electronic warfare library. The Washington Post said it agreed to withhold some details of what was stolen at the request of the U.S. Navy over fears it could compromise national security.

A Navy spokesperson told Fox News in a statement the service branch will not comment on specific incidents, but cyber threats are “serious matters” officials are working to “continuously” bolster awareness of. There are measures in place that require companies to notify the government when a cyber incident has occurred that has actual or potential adverse effects on their networks that contain controlled unclassified information,” Cmdr. Bill Speaks said. “It would be inappropriate to discuss further details at this time.”Military experts fear that China has developed capabilities that could complicate the Navy’s ability to defend US allies in Asia in the event of a conflict with China. The Chinese are investing in a range of platforms, including quieter submarines armed with increasingly sophisticated weapons and new sensors, Admiral Philip Davidson said during his April nomination hearing to lead US Indo-Pacific Command. And what they cannot develop on their own, they steal – often through cyberspace, he said. “One of the main concerns that we have,” he told the Senate Armed Services Committee, “is cyber and penetration of the dot-com networks, exploiting technology from our defense contractors, in some instances.”

Chinese government hackers have previously targeted information on the U.S. military, including designs for the F-35 joint strike fighter which they copied. Last year, South Korean firms involved in the deployment of the U.S. Army’s Terminal High-Altitude Area Defense, or THAAD, missile defense system, the Wall Street Journal reported at the time. No matter how fast the government moves to shore up its cyber defenses, and those of the defense industrial base, the cyber attackers move faster.

Compiled from Jennifer Griffin at Fox News, The Post, The Wall Street Journal, Independent News, and Huff Post. Edited and curated by Jeremy Swenson of Abstract Forward Consulting.

Three Points on Artificial Intelligence and Cyber-Security for 2017

icit-new-logo-for-website5
Although I have been known for longer posts, I would like to offer only three things to watch out for related to artificial intelligence and cyber-security for 2017, followed by sharing two videos.

1) Cyber attackers have long used machine learning and automation techniques to streamline their operations and may soon use full-blown artificial intelligence to do it. Botnets will become self-healing and will be able to detect when they are being discovered and can re-route in response. The botnet and cyber crime business will grow and become more organized. Shodan, the world’s first search engine for internet connected devices, will be used to target companies and individuals negatively. Yet it can also be used for safety and compliance monitoring, most likely when its feed into another analytical tool.

How to Hack with Shodan (For Educational Purposes Only):

2) It won’t be long until A.I. learns the patterns of mutating viruses and then has the ability to predict and/or stop them in their tracks. This is dependent on the most up to date virus definitions, and corresponding algorithms. How a Zero Day is made is heavily a math problem applied to a certain context and operating system. There should be a math formula to predict the next most likely Zero Day exploit – A.I. could provide this. It’s a matter of calculating all possible code various and code add on variations. It’s a lot more advanced than a Rubix Cube.
975f495fafd8c494591892412ecf87e33) A.I. has the potential to close the gap between the lesser developed world and the developed world. The technology behind A.I. is not limited to big companies like IBM or Microsoft for the long term. We may be surprised with tech start-ups out of the lesser developed world who are very creative. Lack of fiber optic cable connectivity has forced many lesser developed nations to rely heavily on cell tower smartphone based internet communications. This has inspired a mobile app growth wave in parts of Africa as described here; “the use of smartphones and tablets within the country has led to a mobile revolution in Nigeria. Essentially, people now tend to seek mobile solutions more often and thus, enhance the growth of the mobile app development industry” (Top 4 Mobile App development companies in Nigeria, IT News Africa, 2015). A.I. will likely close the gap between these two sectors though not drastically change it. If lesser developed countries can build their own mobile apps and outsource things to A.I.; they could become more independent from the economic constraints of the developed world.

The below video highlights some of the complications around these points. It is from a conference hosted by the ICIT on April 25, 2016, and I did not attend this. In the video, Donna Dodson (Associate Director, Chief Cybersecurity Advisor and Director, NIST), Mark Kneidinger (Director, Federal Network Resiliency, DHS), Malcolm Harkins (ICIT Fellow – Cylance) and Stan Wisseman (ICIT Fellow – HPE) discuss related concepts and share realistic examples of how these technologies are reshaping the cyber-security landscape.

ICIT Forum 2016: Artificial Intelligence Enabling Next-Generation Cybersecurity

If you want to contact me to discuss these concepts click here.

Demystifying 9 Common Types of Cyber Risk

1)       Crimeware
This is designed to fraudulently obtain financial gain from either the affected user or third parties by emptying bank accounts, or trading confidential data, etc. Crimeware most often starts with advanced social engineering which results in disclosed info that leads to the crimeware being installed via programs that run on botnets which are zombie computers in distant places used to hide the fraudsters I.P (internet protocol) trail. Usually the victim does not know they have crimeware on their computer until they start to see weird bank charges or the like, or an I.T. professional points it out to them. Often times it masquerades as fake but real looking antivirus software demanding your credit card info in an effort to then commit fraud with that info.

2)       Cyber-Espionage
The term generally refers to the deployment of viruses that clandestinely observe or destroy data in the computer systems of government agencies and large enterprises – unauthorized spying by computer, tablet, or phone. Antivirus maker Symantec described one noteworthy example where the U.S. Gov’t made a worm to disable Iran’s nuclear reactors arguably in the name of international security (Fig. 1).

“Stuxnet is a computer worm that targets industrial control systems that are used to monitor and control large scale industrial facilities like power plants, dams, waste processing systems and similar operations. It allows the attackers to take control of these systems without the operators knowing. This is the first attack we’ve seen that allows hackers to manipulate real-world equipment, which makes it very dangerous. It’s like nothing we’ve seen before – both in what it does, and how it came to exist. It is the first computer virus to be able to wreak havoc in the physical world. It is sophisticated, well-funded, and there are not many groups that could pull this kind of threat off. It is also the first cyberattack we’ve seen specifically targeting industrial control systems” (Accessed 03/20/16, Norton Stuxnet Review).

Richard Clarke is the former National Coordinator for Security, Infrastructure Protection and Counter-terrorism for the United States and he commentated on Stuxnet and cyber war generally in this Economist Interview from 2013.

Fig.1.

3)       Denial of Service (DoS) Attacks
A DoS attack attempts to deny legitimate users access to a particular resource by exploiting bugs in a specific operating system or vulnerabilities in the TCP/IP implementation (internet protocols) via a botnet of zombie computers in remote areas (Fig. 2). This allows one host (usually a server or router) to send a flood of network traffic to another host (Fig. 3.). By flooding the network connection, the target machine is unable to process legitimate requests for data. Thus the targeted computers may crash or disconnect from the internet from resource exhaustion – consuming all bandwidth or disk space, etc (Fig. 3.). In some cases they are not very harmful, because once you restart the crashed computer everything is on track again; in other cases they can be disasters, especially when you run a corporate network or ISP (internet service provider).
Fig. 2.                                                                Fig. 3.Botnet and TCP image
4)      
Insider and Privilege Misuse
Server administrators, network engineers, outsourced cloud workers, developers, I.T. security workers, and database administrators  are given privileges to access many or all aspects of a company’s IT infrastructure. Companies need these privileged users because they understand source code, technical architecture, file systems and other assets that allow them to upgrade and maintain the systems; yet this presents a potential security risk.

With the ability to easily get around controls that restrict other non-privileged users they sometimes abuse what should be temporary access privileges to perform tasks. This can put customer data, corporate trade secrets, and unreleased product info at risk. Savvy companies implement multi-layered approvals, advanced usage monitoring,  2 or 3 step authentication, and a strict need to know policy with an intelligible oversight process.

5)       Miscellaneous Errors
This is basically an employee or customer doing something stupid and unintentional that results in a partial or full security breach of an information asset. This does not include lost devices as that is grouped with theft – this is a smaller category. The 2014 Verizon Enterprise Data Breach Investigation Report gives an example of this category as follows:

“Misdelivery (sending paper documents or emails to the wrong recipient) is the most frequently seen error resulting in data disclosure. One of the more common examples is a mass mailing where the documents and envelopes are out of sync (off-by-one) and sensitive documents are sent to the wrong recipient” (Accessed 02/21/16, Page 29).

6)       Payment Card Skimmers
This is a method where thieves steal your credit card information at the card terminals, often at bars, restaurants, gas stations, sometimes at bank ATMs, and especially where there is low light, no cameras, or anything to discourage the criminal from tampering with the card terminal.

Corrupt employees can have a skimmer stashed out of sight or crooks can install hidden skimmers on a gas pump. Skimmers are small devices that can scan and save credit card data from the magnetic stripe (Fig. 4.). After the card slides through the skimmer, the data is saved, and the crooks usually then sell the information through the internet or if they really want to be secure the Darknet which is a secure non-mainstream internet that requires a special browser or plug-in to access. After this counterfeit cards are made, then bogus charges show up, and the bank eats the costs which unfortunately drives up the cost of banking for everyone else. Also, some skimmers have mini cameras which record the pin numbers typed at ATM machines for a more aggressive type of fraud (Fig. 5.).  Here are two images of skimmer technologies:

Fig 4.                                                                       Fig 5.
Card Skimmer and Camera

7)       Physical Theft and Loss
This includes armed robbery, theft by accident, and/or any type of device or data lost.  Although some of the stolen or lost items may never end up breached or used for fraud sometime they are depending on what device and/or what data is on that device and/or if it was encrypted or not, or if it the data could be deleted remotely, etc.

8)       Point of Sale Intrusions
See my 2014 post on the Target Data Breach here for a good example.

9)       Web App Attacks
These incidents were carried out primarily via manipulation of vulnerabilities in input validation and authentication affecting common content management systems like Joomla, Magento, SiteCore, WordPress, and Drupal.

According to the 2015 Verizon Data Breach Investigation Report these types of attacks are not only a reliable method for hackers, but also fast with 60% of the compromises taking a few minutes or less(Accessed 02/21/16). With web applications commonly serving as an organization’s public face to the Internet, the ease of exploiting web-based vulnerabilities is alarming (Accessed 02/21/16, 2015 Verizon Data Breach Investigation Report). According to The Open Web Application Security Project these are two common types Web App weaknesses (Accessed 02/21/16, 2013, OWASP 10 Most Critical Web Application Security Risks):

“i) Injection flaws, such as SQL, OS, and LDAP injection occur when untrusted data is sent to an interpreter as part of a command or query. The attacker’s hostile data can trick the interpreter into executing unintended commands or accessing data without proper authorization.

ii) XSS flaws occur whenever an application takes untrusted data and sends it to a web browser without proper validation or escaping (Fig. 6.). XSS allows attackers to execute scripts in the victim’s browser which can hijack user sessions, deface web sites, or redirect the user to malicious sites access unauthorized pages”.

Fig. 6.
RXSS
Jeremy Swenson, MBA is a seasoned, Intel certified, retail technology marketing and training representatives on assignment at Best Buy for clients including Intel, Trend Micro, Adobe, and others. He also doubles as a Sr. business analyst and project management consultant. Tweet to him @jer_Swenson.